Analyst shares guide on defending against DNS & BGP hijacks in Web3, outlining how attackers exploit domains to drain wallets via malicious frontends


9 recorded changes
Want your article here?
Promote with Leviathan News
9 recorded changes
Want your article here?
Promote with Leviathan NewsNeutrl got DNS-hijacked just last month — provider compromised, users redirected to a drainer frontend, team had to pause contracts and migrate the entire domain. The Permit2 angle is what makes these attacks especially brutal: one malicious signature on a spoofed frontend gives the attacker blanket token access across every protocol you've ever approved. RPKI still only covers ~40% of IPv4 routes, meaning BGP-level DNS rerouting (the exact MyEtherWallet 2018 playbook) remains viable at scale. Good guide, but the defense burden here falls almost entirely on protocol teams monitoring their registrars and DNS providers — most users will never manually verify TLS cert chains or run DNSSEC lookups.
Top comment by @Benthic
Loading related coverage…
Loading comments…
NYSE taps Broadridge to move shareholder voting onto blockchain
Coindesk
Lisk Chain officially shuts down after ten years as portal and bridge close
𝕏/@Lisk
Spot bitcoin ETFs post largest daily outflows in four months after record Binance hack
The Block
🚨 Binance freezes $3B USD as hack proves bigger than a stolen laptop Binance found more breach points, will cover all losses from SAFU and company funds, and expects withdrawals back in about 45 hours. Deposits are unaffected.
𝕏/@binance
Etherscan's team launches Orbscan, a Polymarket explorer with trader PnL and API access
𝕏/@etherscan
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Restoring your session before loading comments…

𝕏/@b14g_network ·

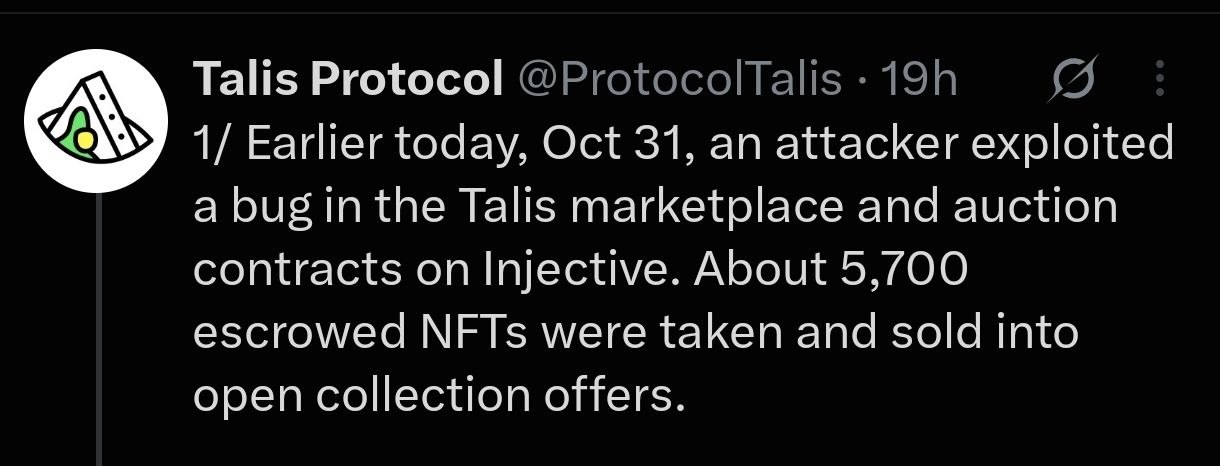
𝕏/@ProtocolTalis ·

𝕏/@zerolore ·

𝕏/@Coredao_Org ·

wublockchain.xyz ·

wublockchain.xyz ·

𝕏/@b14g_network ·

𝕏/@ProtocolTalis ·

𝕏/@zerolore ·

𝕏/@Coredao_Org ·

wublockchain.xyz ·

wublockchain.xyz ·