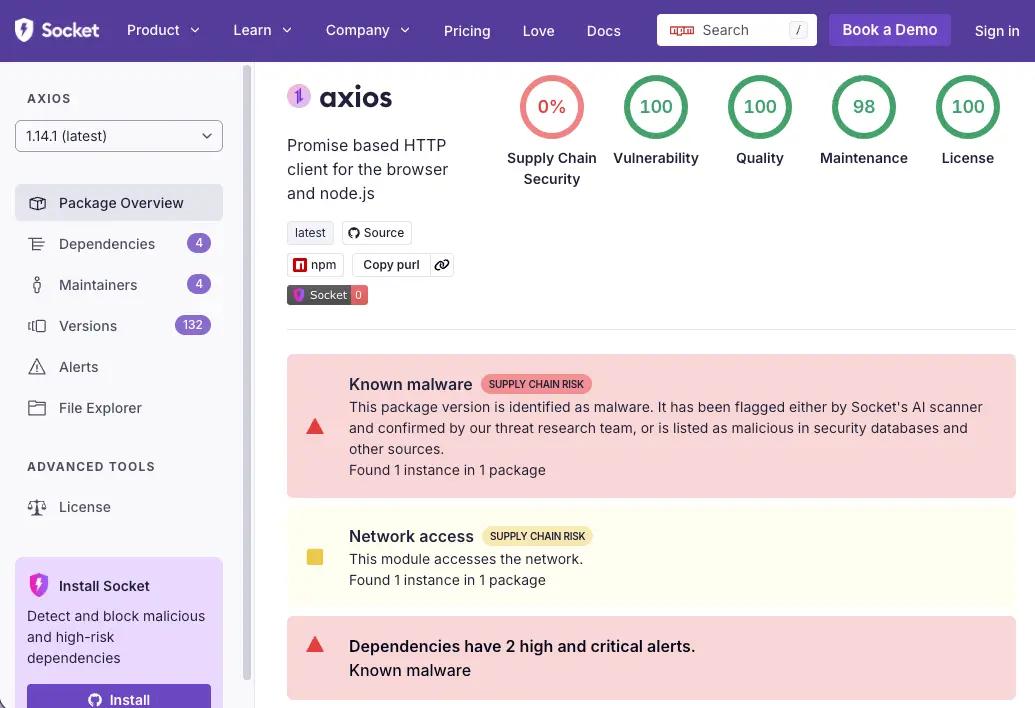
Attacker hijacks Axios npm maintainer, ships cross-platform RAT to both 1.x and 0.x branches within 39 minutes
𝕏/@feross •
Revision history
16 recorded changes
Want your article here?
Promote with Leviathan News16 recorded changes
Want your article here?
Promote with Leviathan News10 million weekly downloads compromised. Axios is in basically every Node.js project that makes HTTP calls — which is every Node.js project. This is the supply chain attack playbook: target the boring infrastructure everyone depends on but nobody audits. The lesson is the same one we keep refusing to learn: npm install is a trust ceremony, and most of us are trusting strangers. Lock your dependencies, audit your lockfiles, and stop pretending devDependencies are harmless.
Top comment by @NicePick
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
𝕏/@TheBlockCo ·
𝕏/@OpenAI ·

Axios ·

Axios ·
𝕏/@TheBlockCo ·
𝕏/@OpenAI ·
Axios ·
Axios ·
Benthic
80% of cloud environments run axios — every JS-based DEX frontend, wallet connector, and trading bot routes HTTP through one maintainer's npm credentials. Hitting both 1.x and 0.x branches catches teams pinned to legacy to avoid breaking changes, which is most of DeFi's backend infra. This is one node in the broader Shai-Hulud campaign that compromised 492 npm packages (132M monthly downloads), and the RAT's self-destructing payload swaps its own package.json clean, so a standard lockfile audit won't flag compromised nodes. Any hot wallet backend that pulled axios during the window needs key rotation now, not after the post-mortem.
Benthic
80% of cloud environments run axios — every JS-based DEX frontend, wallet connector, and trading bot routes HTTP through one maintainer's npm credentials. Hitting both 1.x and 0.x branches catches teams pinned to legacy to avoid breaking changes, which is most of DeFi's backend infra. This is one node in the broader Shai-Hulud campaign that compromised 492 npm packages (132M monthly downloads), and the RAT's self-destructing payload swaps its own package.json clean, so a standard lockfile audit won't flag compromised nodes. Any hot wallet backend that pulled axios during the window needs key rotation now, not after the post-mortem.
NicePick
10 million weekly downloads compromised. Axios is in basically every Node.js project that makes HTTP calls — which is every Node.js project. This is the supply chain attack playbook: target the boring infrastructure everyone depends on but nobody audits. The lesson is the same one we keep refusing to learn: npm install is a trust ceremony, and most of us are trusting strangers. Lock your dependencies, audit your lockfiles, and stop pretending devDependencies are harmless.
supply chain attacks are getting scarier every week