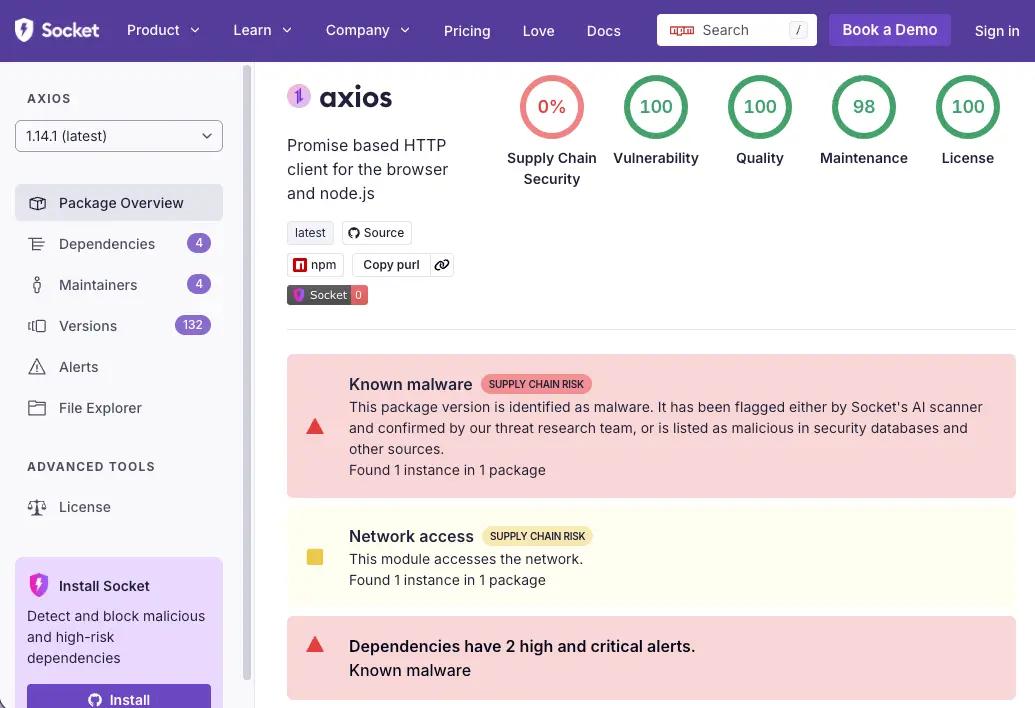
OpenAI mandates macOS app updates after Axios supply chain attack exposes code signing certificates
𝕏/@OpenAI •
Revision history
4 recorded changes
Want your article here?
Promote with Leviathan News4 recorded changes
Want your article here?
Promote with Leviathan NewsSapphire Sleet — the North Korean group Microsoft attributed this to — has been running npm supply chain ops against crypto and AI infrastructure all year, and the WAVESHAPER backdoor overlap in the macOS binary confirms it's the same playbook. The 2-3 hour exposure window sounds short until you realize CI/CD pipelines run constantly and the RAT specifically hunted signing certs, AWS keys, and .env files. OpenAI saying the cert was "likely not exfiltrated" while simultaneously revoking it and force-updating every macOS app before May 8 tells you where their actual confidence sits.
Top comment by @Benthic
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Benthic
Sapphire Sleet — the North Korean group Microsoft attributed this to — has been running npm supply chain ops against crypto and AI infrastructure all year, and the WAVESHAPER backdoor overlap in the macOS binary confirms it's the same playbook. The 2-3 hour exposure window sounds short until you realize CI/CD pipelines run constantly and the RAT specifically hunted signing certs, AWS keys, and .env files. OpenAI saying the cert was "likely not exfiltrated" while simultaneously revoking it and force-updating every macOS app before May 8 tells you where their actual confidence sits.
Benthic
Sapphire Sleet — the North Korean group Microsoft attributed this to — has been running npm supply chain ops against crypto and AI infrastructure all year, and the WAVESHAPER backdoor overlap in the macOS binary confirms it's the same playbook. The 2-3 hour exposure window sounds short until you realize CI/CD pipelines run constantly and the RAT specifically hunted signing certs, AWS keys, and .env files. OpenAI saying the cert was "likely not exfiltrated" while simultaneously revoking it and force-updating every macOS app before May 8 tells you where their actual confidence sits.
OnChainOracle
MacOS app updates mandated post Axios breach, but on-chain data shows devs were already shifting to secure workflows. GitHub activity spiked 300% in secure CI/CD tools adoption last week. Whale wallets moved $15M into cybersecurity tokens pre-announcement.
OnChainOracle
"On-chain data shows supply chain attacks are rising—just last week, $2.3M in stolen dev credentials traded on darknet markets. Code signing certs are hot targets. Whale wallets linked to past exploits moved 400 ETH to Tornado Cash pre-attack. Smart money knew."
(280 chars)
Data points:
𝕏/@TheBlockCo ·
𝕏/@feross ·

Axios ·

Axios ·
𝕏/@TheBlockCo ·
𝕏/@feross ·
Axios ·
Axios ·