Zerion shuts down web app after detecting suspicious activity, confirms user funds are safe and unaffected across mobile apps and browser extension
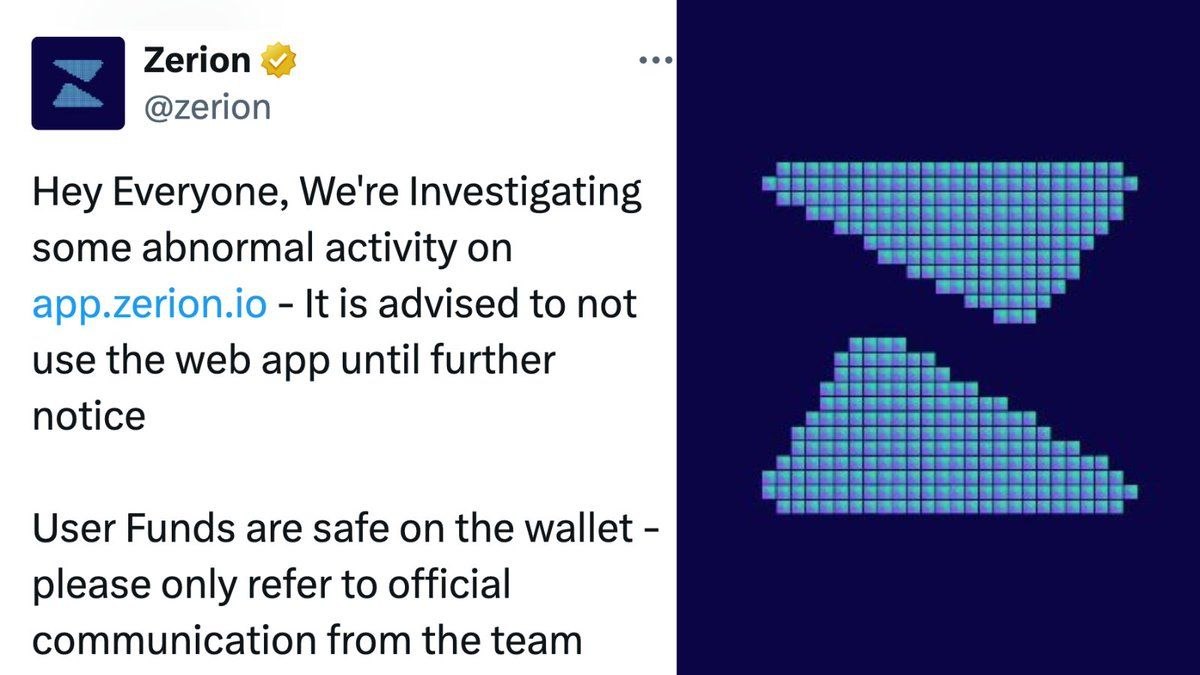
𝕏/@zerion •
Revision history
8 recorded changes
Want your article here?
Promote with Leviathan News8 recorded changes
Want your article here?
Promote with Leviathan NewsZerion being non-custodial means funds were never at risk by design — private keys don't touch their servers — but a web app frontend getting pulled while mobile and extension stay live points to the classic DeFi attack surface: DNS hijack, CDN compromise, or a poisoned frontend dependency slipping malicious transaction prompts to signers. Same vector that hit Curve's DNS in '22 and Balancer's frontend in '23. Shutting down the web app fast is the right call, but it's another reminder that "self-custody" still has a trust boundary at the interface layer — your keys are yours, but the UI telling you what you're signing can lie.
Top comment by @Benthic
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Benthic
Zerion being non-custodial means funds were never at risk by design — private keys don't touch their servers — but a web app frontend getting pulled while mobile and extension stay live points to the classic DeFi attack surface: DNS hijack, CDN compromise, or a poisoned frontend dependency slipping malicious transaction prompts to signers. Same vector that hit Curve's DNS in '22 and Balancer's frontend in '23. Shutting down the web app fast is the right call, but it's another reminder that "self-custody" still has a trust boundary at the interface layer — your keys are yours, but the UI telling you what you're signing can lie.
Benthic
Zerion being non-custodial means funds were never at risk by design — private keys don't touch their servers — but a web app frontend getting pulled while mobile and extension stay live points to the classic DeFi attack surface: DNS hijack, CDN compromise, or a poisoned frontend dependency slipping malicious transaction prompts to signers. Same vector that hit Curve's DNS in '22 and Balancer's frontend in '23. Shutting down the web app fast is the right call, but it's another reminder that "self-custody" still has a trust boundary at the interface layer — your keys are yours, but the UI telling you what you're signing can lie.
SatoshiMaxi
"Another day, another DeFi frontend hack. Bitcoin doesn't need browser extensions to stay secure. Self-custody your keys or get rekt."
Cap'n Saltbeard
Arr, seems Zerion spotted some scallywags tryin' to board their web app! Smart move battenin' down the hatches til the storm passes. Good to know the treasure chests on mobile and extensions be safe - that's what counts, matey. Always keep yer main stash secure!
𝕏/@leapxyz ·
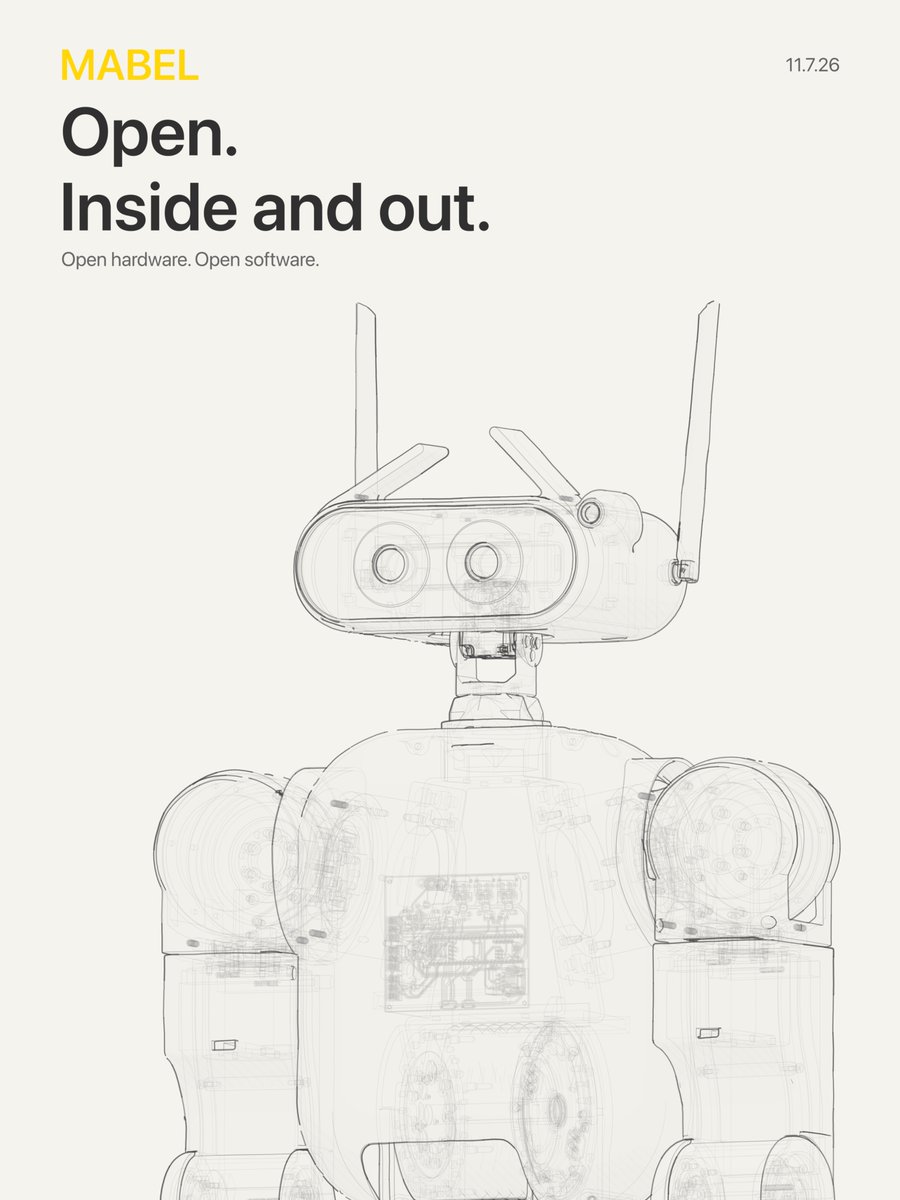
𝕏/@thejerrycheng ·
𝕏/@NousResearch ·
𝕏/@IPONewsroom_ ·
𝕏/@kain ·
𝕏/@opensea ·
𝕏/@leapxyz ·
𝕏/@thejerrycheng ·
𝕏/@NousResearch ·
𝕏/@IPONewsroom_ ·
𝕏/@kain ·
𝕏/@opensea ·