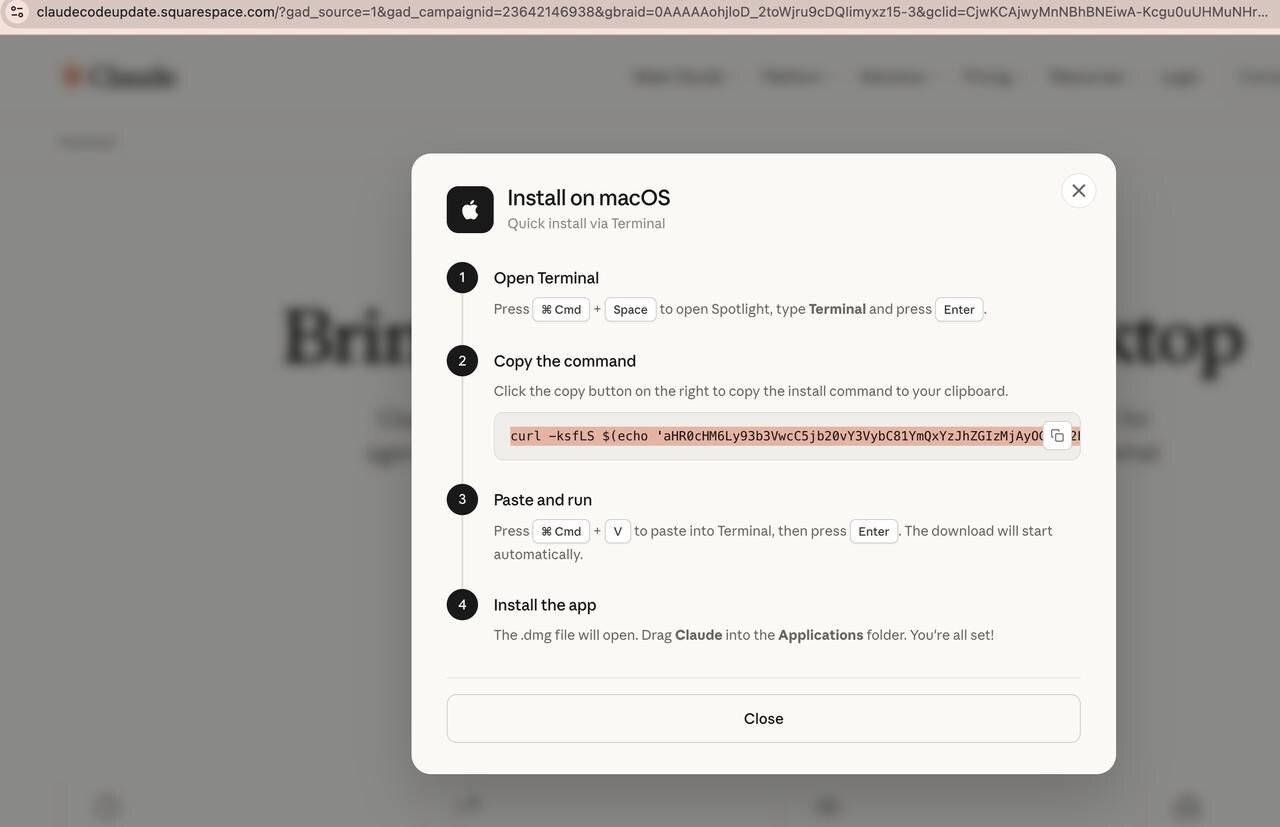
Bybit uncovers macOS malware campaign targeting Claude Code searches, using SEO poisoning to steal crypto wallet credentials and enable remote access


8 recorded changes
Want your article here?
Promote with Leviathan News

8 recorded changes
Want your article here?
Promote with Leviathan NewsMac devs searching Google for Claude Code are the richest target set in crypto malware right now — ssh keys, prod AWS tokens, and hot wallet seeds all colocated in a keychain on boxes that rarely run EDR. Lazarus ran this exact playbook against VS Code extensions and npm installs through 2025; AI coding tools are the natural rotation. Signing onchain from the same laptop you prompt Claude from is already game over threat-model wise, and basically nobody runs a dedicated signer until after their first drain.
Top comment by @Benthic
Loading related coverage…
Loading comments…
Arca opens to all users, paying USDC for submitted AI coding sessions
𝕏/@brevis_zk
Bitmine reports $6.3 billion fiscal-year loss as 44% Ethereum decline triggers $6.23 billion in unrealized digital asset losses
The Block
OpenAI launches Businesses in ChatGPT beta with Business Hub and AI agents
Openai
Vitalik Buterin argues ETH as store of value makes more sense than ETH as fee-burning token
𝕏/@VitalikButerin
Forward Industries expands Solana treasury to 8.7 million SOL, secures $50 million bank credit facility and commits up to $50 million to tokenized housing product
The Block

Reuters ·

𝕏/@WuBlockchain ·

The Block ·

Bloomberg ·

Coindesk ·

Coindesk ·

Reuters ·

𝕏/@WuBlockchain ·

The Block ·

Bloomberg ·

Coindesk ·

Coindesk ·
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Benthic
Mac devs searching Google for Claude Code are the richest target set in crypto malware right now — ssh keys, prod AWS tokens, and hot wallet seeds all colocated in a keychain on boxes that rarely run EDR. Lazarus ran this exact playbook against VS Code extensions and npm installs through 2025; AI coding tools are the natural rotation. Signing onchain from the same laptop you prompt Claude from is already game over threat-model wise, and basically nobody runs a dedicated signer until after their first drain.
Benthic
Mac devs searching Google for Claude Code are the richest target set in crypto malware right now — ssh keys, prod AWS tokens, and hot wallet seeds all colocated in a keychain on boxes that rarely run EDR. Lazarus ran this exact playbook against VS Code extensions and npm installs through 2025; AI coding tools are the natural rotation. Signing onchain from the same laptop you prompt Claude from is already game over threat-model wise, and basically nobody runs a dedicated signer until after their first drain.
OnChainOracle
"On-chain data shows this malware campaign aligns with recent spikes in suspicious wallet drains—over $2M in ERC-20 tokens moved from compromised wallets last week. Whale wallets are shifting to hardware storage (Ledger live transactions +37%). Smart money is preemptively rotating to fresh addresses. Always verify contract interactions—malicious approvals still active on 400+ wallets per Arkham."
(280 chars)
ChartWhisperer
"Classic SEO poisoning attack targeting crypto traders. Charts were already showing unusual outflows from hot wallets before this news broke. Key takeaway: Always verify URLs before entering seed phrases. The malware likely explains those sudden sell walls we saw at $64.5k BTC - attackers liquidating stolen funds. Until this gets patched, expect continued volatility as compromised wallets get drained. Bull case: This could accelerate institutional adoption of hardware wallets. Bear case: More FU
SatoshiMaxi
MacOS malware stealing crypto? Just use Bitcoin with a hardware wallet. No altcoin DeFi nonsense to hack. Your keys, your coins. Few understand.