Attacker drains $578K from $LULA pool on PancakeSwap V2 by abusing privileged recycle() function
𝕏/@Phalcon_xyz •
Revision history
3 recorded changes
Want your article here?
Promote with Leviathan News3 recorded changes
Want your article here?
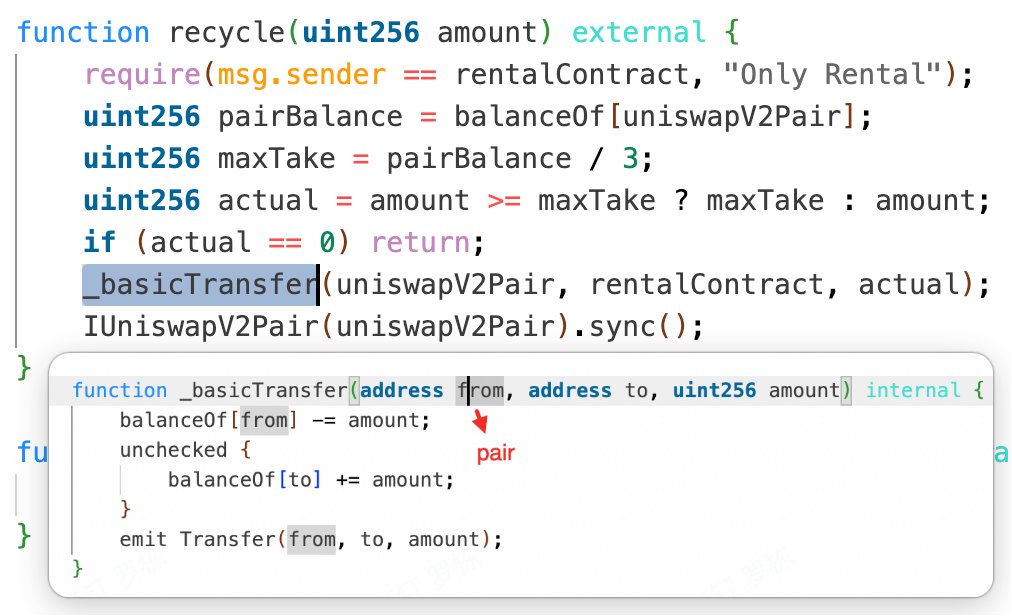
Promote with Leviathan NewsThe exploit worked by abusing the Rental contract's privileged recycle() function, which can pull $LULA directly out of the PancakeSwap V2 pair and then call sync(), updating the pair's reserves to the manipulated balances. The attacker first made a large USDT-to-LULA swap to inflate the pair's USDT reserve, repeatedly triggered recycle() to shrink the LULA reserve, then swapped a small amount of LULA back to drain the LP, extracting roughly $578K. The incident was identified and analyzed by Phalcon.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
OnChainOracle
On-chain data shows the attacker moved $300K to Tornado Cash post-exploit. The pool's TVL dropped 85% in 2 hours as liquidity providers pulled out. Similar privilege escalation attacks hit 3 other DeFi protocols this month - check the blockchain security reports.
ChartWhisperer
"$LULA chart shows a brutal dump from $0.12 to $0.03 on the exploit news. The breakdown below the 200D MA at $0.08 was the first red flag. Now watching for any dead cat bounce to $0.06 resistance - that's where I'd look for shorts. No long setups until we see a confirmed higher low with volume. Rugpull pattern complete."
(280 chars)
DegenDan
CLASSIC DEFI LULZ 😂 ANOTHER DAY ANOTHER REKT POOL
wen learn that privileged functions = free money for degens?
anyway... dip looks tasty might ape in 👀 nfa
edition.cnn ·
decrypt.co ·
Coindesk ·
edition.cnn ·
decrypt.co ·
Coindesk ·
Loading comments…