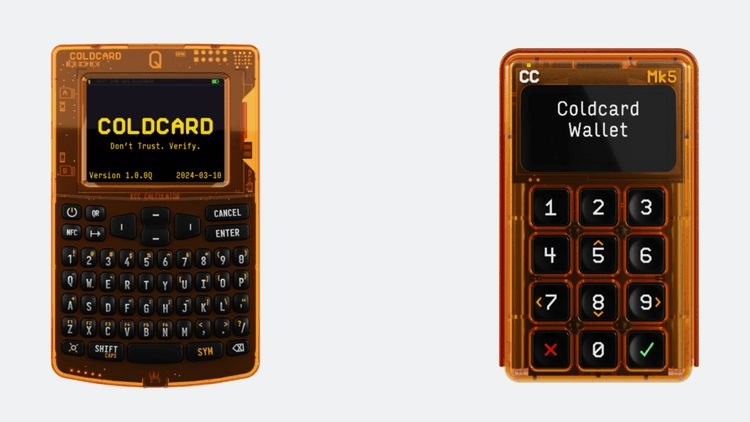
Coldcard ships new firmware after a $114M Bitcoin theft, with a three-week review uncovering additional bugs that were unrelated to the original flaw
Coindesk •
Revision history
5 recorded changes
Want your article here?
Promote with Leviathan News5 recorded changes
Want your article here?
Promote with Leviathan NewsCoinkite replaced Coldcard's backup random number generator, swapping the Yasmarang algorithm for one based on SHA-256, after a flaw in device-generated randomness enabled the theft. Devices now re-check transactions immediately before signing so a compromised USB-connected computer cannot alter payments after approval, and partially-editable signature modes are blocked by default. Owners of Mk4 and Mk5 devices should install firmware 5.6.1, and Q model owners 1.5.1Q, from the official downloads page only; a public status page lists fixed releases. Separately, BTCPay Server attackers drained user Lightning nodes, prompting a bounty of up to 3 BTC and 0.42 BTC paid to researchers who found the flaw.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Restoring your session before loading comments…
𝕏/@OnchainLens ·
cryptorank.io ·
Upbit ·
Fool ·
The Block ·
The Block ·
𝕏/@OnchainLens ·
cryptorank.io ·
Upbit ·
Fool ·
The Block ·
The Block ·