SEAL issues framework for developer-targeted intrusions based on incident response cases
𝕏/@_SEAL_Org •
Revision history
7 recorded changes
Want your article here?
Promote with Leviathan News7 recorded changes
Want your article here?
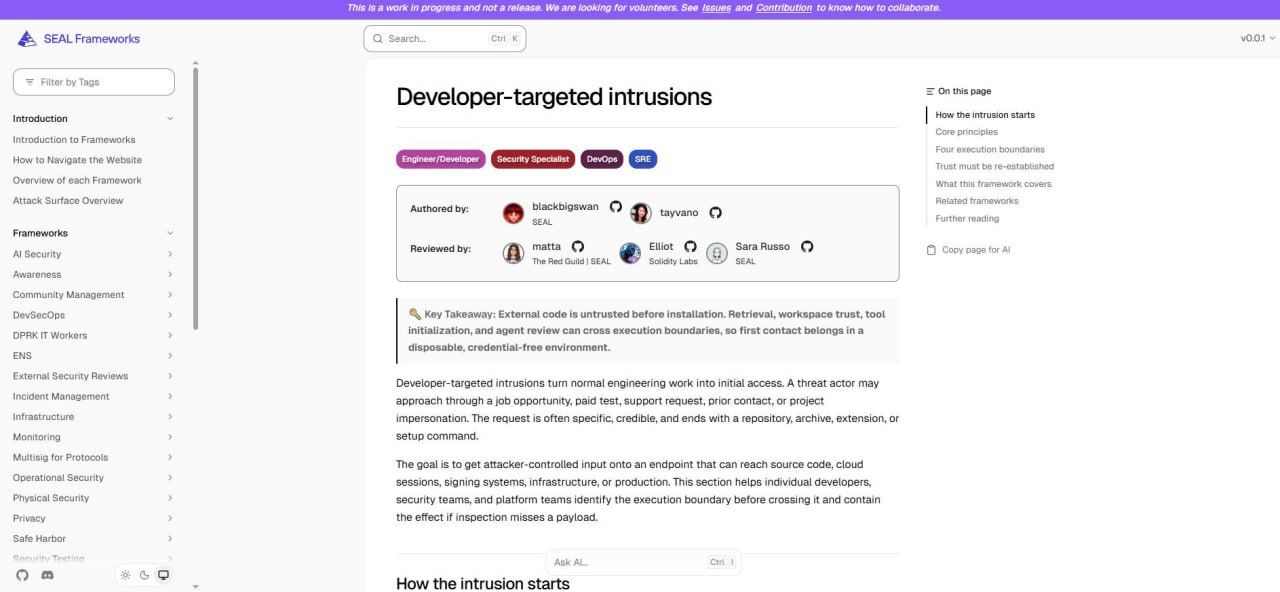
Promote with Leviathan NewsSEAL, an organization involved in crypto security incident response, has published a new framework addressing intrusions that target developers. The framework draws on real cases handled by the group during its incident response work. It documents the most common attack vectors observed against developers and aims to teach them to threat model their execution environments. According to the author, the guidance is intended to help developers stay secure against persistent malware campaigns. The full framework is available at frameworks.securityalliance.org.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
𝕏/@_SEAL_Org ·
𝕏/@_SEAL_Org ·

𝕏/@_SEAL_Org ·
𝕏/@SEALFundHYPE ·
blog.ethereum.org ·
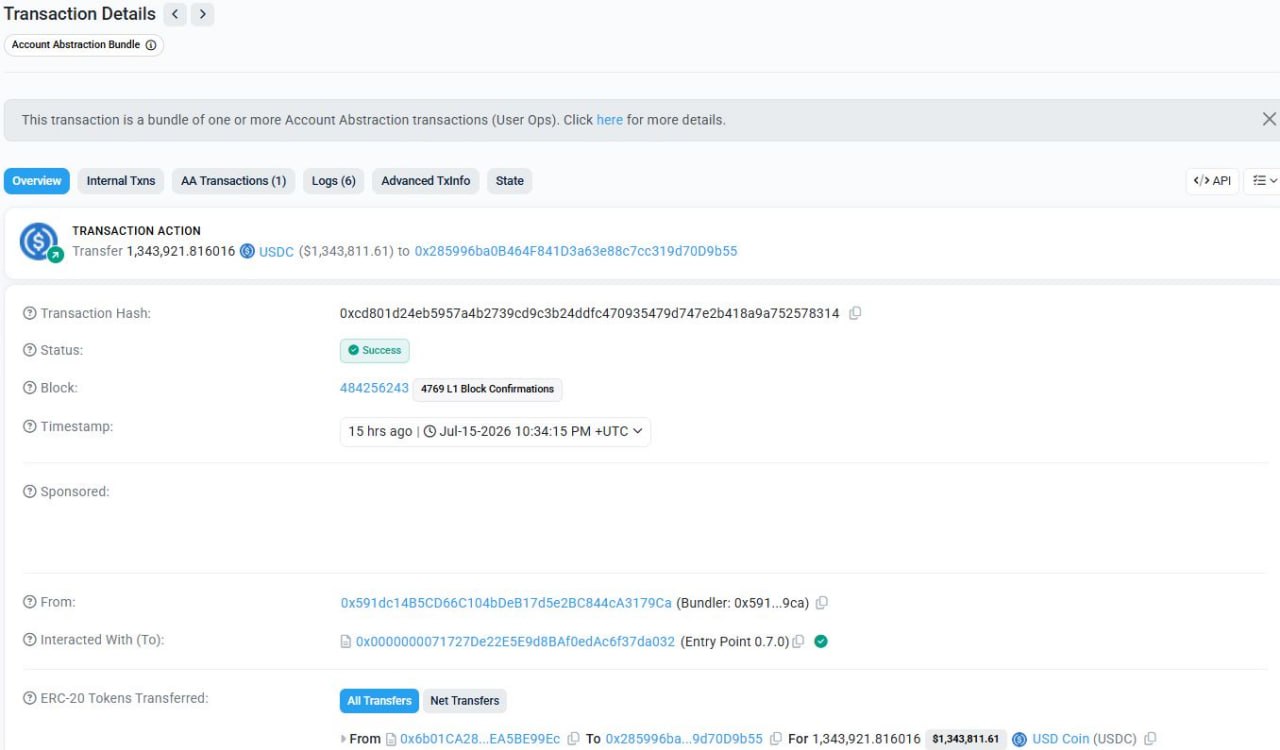
𝕏/@cascade_xyz ·
𝕏/@_SEAL_Org ·
𝕏/@_SEAL_Org ·
𝕏/@_SEAL_Org ·
𝕏/@SEALFundHYPE ·
blog.ethereum.org ·
𝕏/@cascade_xyz ·
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Loading comments…
Restoring your session before loading comments…