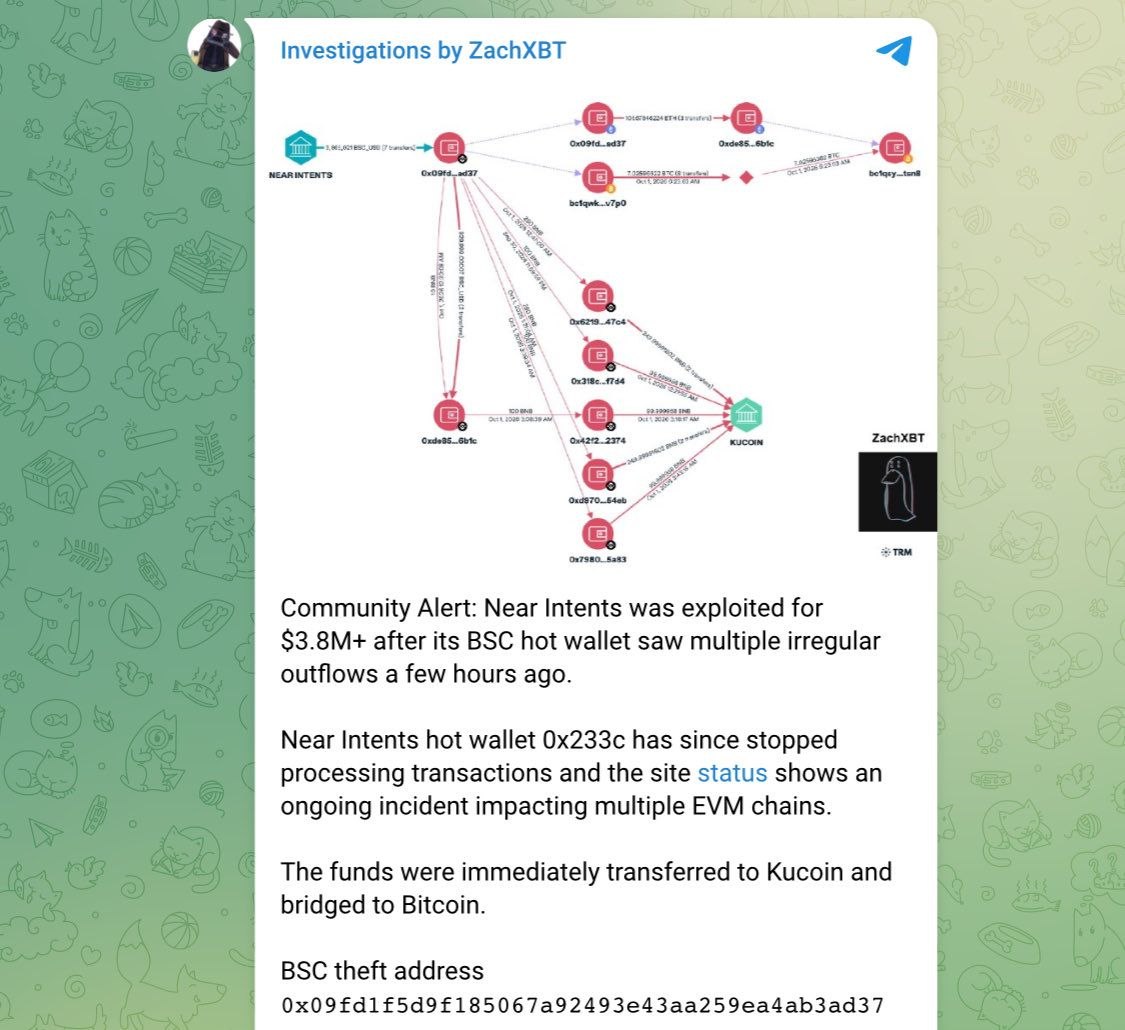
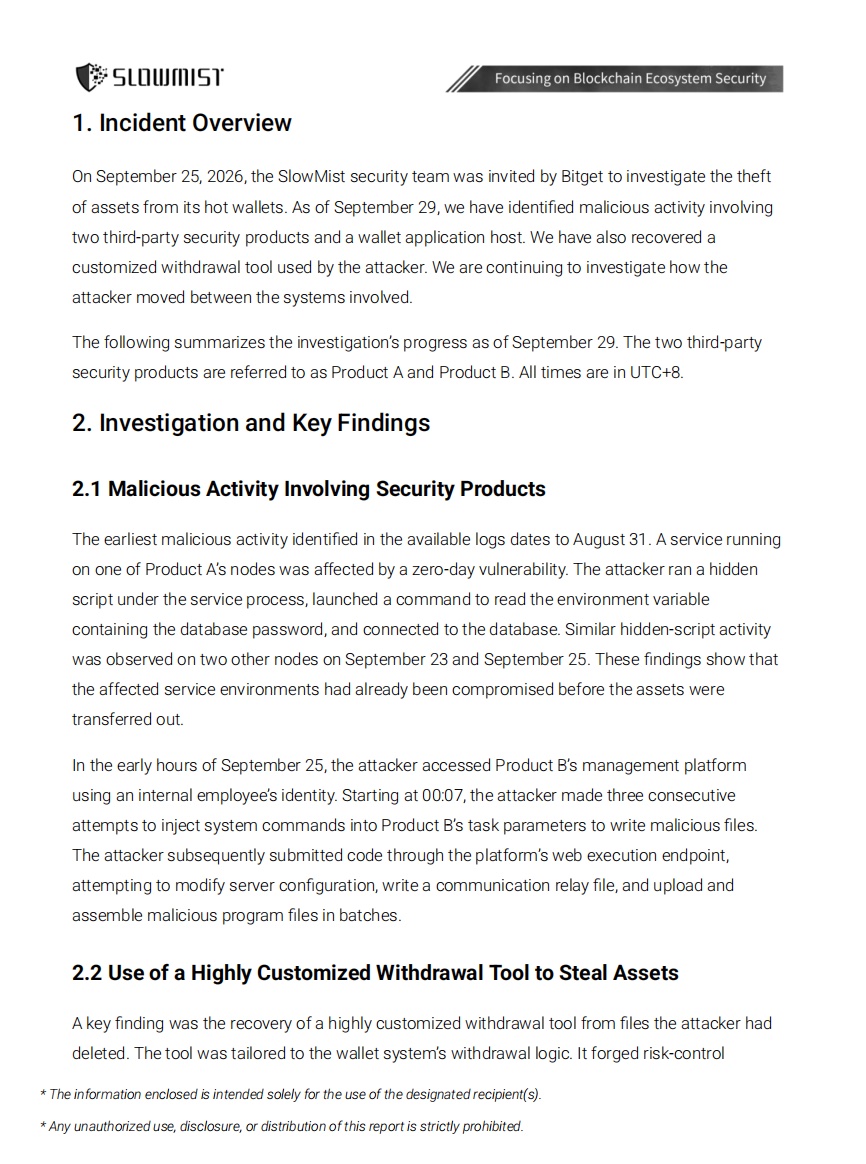
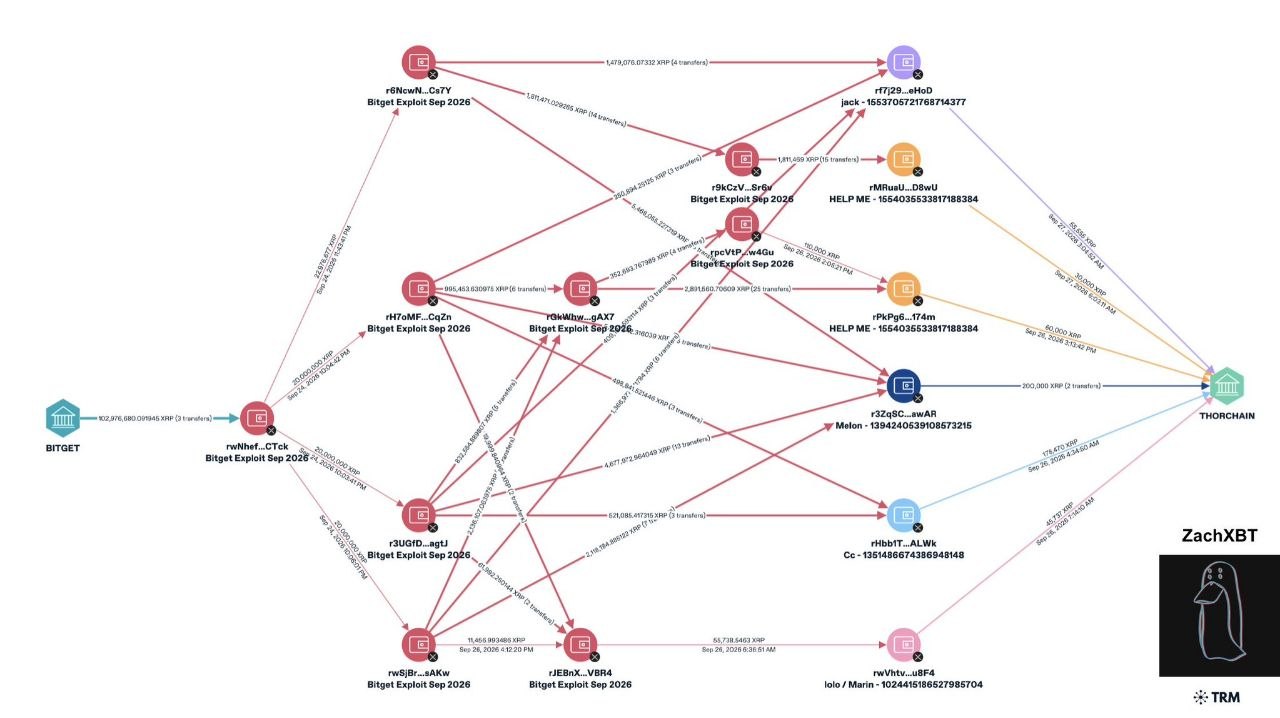
CoinGecko’s 2026 Crypto Security Report finds $3.63B stolen across 245 incidents, with supply-chain attacks, smart contract exploits and key compromises leading losses
𝕏/@bobbyong •
Revision history
6 recorded changes
Want your article here?
Promote with Leviathan News