Linux kernel flaw allows root access, proof of concept demonstrated in labs
𝕏/@tobi •
Revision history
5 recorded changes
Want your article here?
Promote with Leviathan News5 recorded changes
Want your article here?
Promote with Leviathan Newsfirst post
Leviathan +3 d later
All times UTC.
Important notice for the Bitcoin community: if you are running lnd on Linux, and it has open ports, you should shut it down until you patch your Linux kernel or otherwise mitigate CVE-2026-98432. Not lnd's fault. But there's a Linux kernel exploit with mptcp that is relevant.
JUST IN: Linux kernel vulnerability in the golang MPTCP, allowing for remote code execution (RCE), is announced. Bitcoin developer Peter Todd urges all LND noderunners using Linux to shut down or upgrade their kernel ASAP https://t.co/R6QQhdve8r
🚨 PSA for anyone running a Linux server, node, or relay CVE-2026-98432 is a critical Linux kernel bug (CVSS 9.8). Someone on the internet can send crafted TCP packets and take over your machine. No login needed. Ubuntu and Red Hat haven't shipped a fixed kernel yet. Debian,…
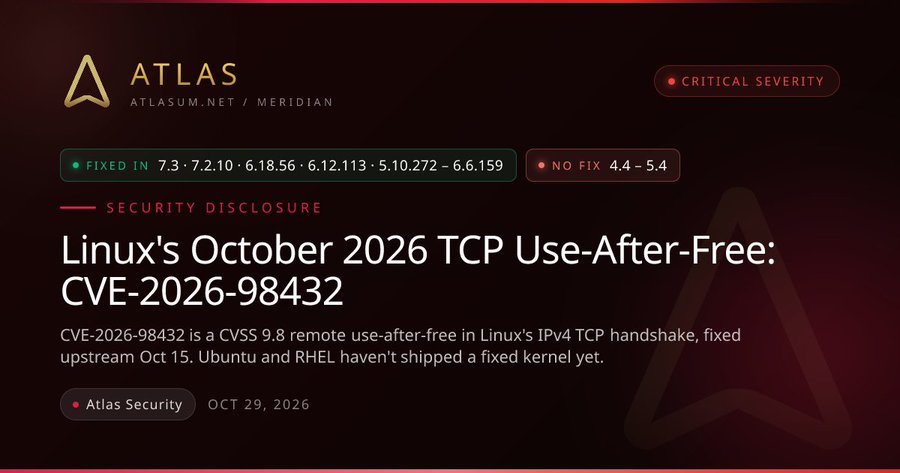
A flaw in the Linux kernel's TCP code, tracked as CVE-2026-98432, affects Ubuntu, Red Hat Enterprise Linux (RHEL), and other Linux distributions. The kernel's own CVE team rates it 9.8 out of 10 on the CVSS scale. Anthropic said on October 27 that its AI model wrote an exploit… https://t.co/IgvFtLuVWx
I spent the last few hours going down the CVE-2026-98432 Critical Linux Kernel Flaw rabbit hole 🕳️ and here are a few thoughts: - It is legit and scary. Kinda crazy that it's been known for 2 weeks & there is still no patch for popular distros (the Ubuntu fix, for example, is…
PSA for anyone running a Linux server, node, or relay CVE-2026-98432 is a critical Linux kernel bug (CVSS 9.8). Someone on the internet can send crafted TCP packets and take over your machine. No login needed.https://t.co/tNMpjtdee0
7 more accounts posted about this
Social-monitoring data, not investment advice Elfa post text from Xas of
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Restoring your session before loading comments…