Premia Labs vaults on Arbitrum exploited for over $400,000 through empty option pools, GoPlus reports
𝕏/@GoPlusSecurity •
Revision history
3 recorded changes
Want your article here?
Promote with Leviathan News3 recorded changes
Want your article here?
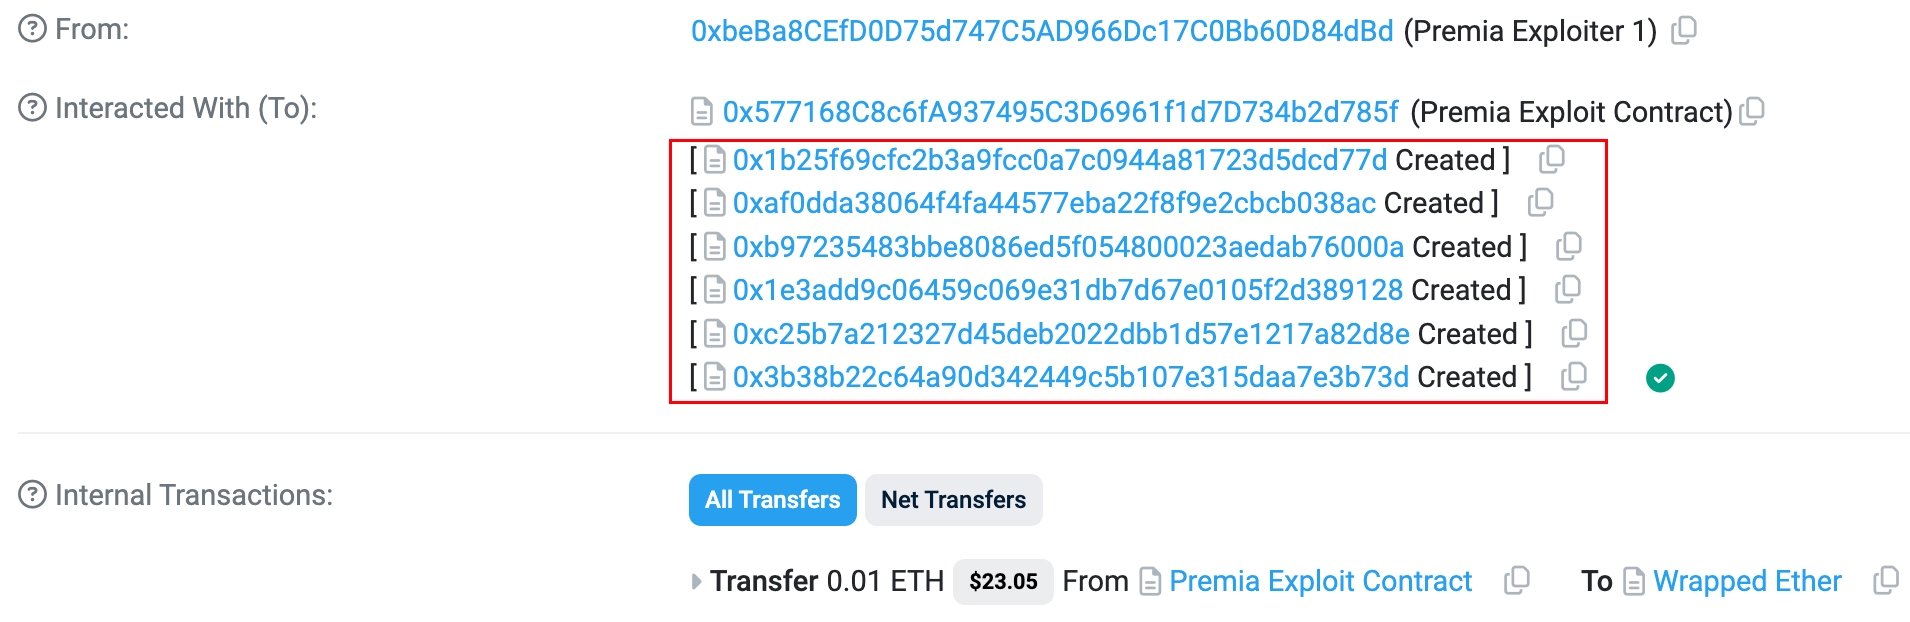
Promote with Leviathan NewsGoPlus's postmortem attributes the exploit to vaults that only verified pools came from the official factory, without checking liquidity, age, or ownership. The attacker deployed six empty pools, then used flash loans to buy options, triggering vaults to lock collateral into those pools, and withdrew it via pool-side accounting. In one WBTC vault, 3.76125 WBTC of collateral was locked and 4.4904 WBTC withdrawn. The same pattern drained ARB call and put vaults in a second transaction, with attacker addresses and six affected vault contracts listed. The attack occurred on November 1 on Arbitrum.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Restoring your session before loading comments…
chainwire.org ·
𝕏/@THORChain ·
𝕏/@blockaid_ ·
Prnewswire ·
𝕏/@KeyringNetwork ·
𝕏/@blockaid_ ·
chainwire.org ·
𝕏/@THORChain ·
𝕏/@blockaid_ ·
Prnewswire ·
𝕏/@KeyringNetwork ·
𝕏/@blockaid_ ·