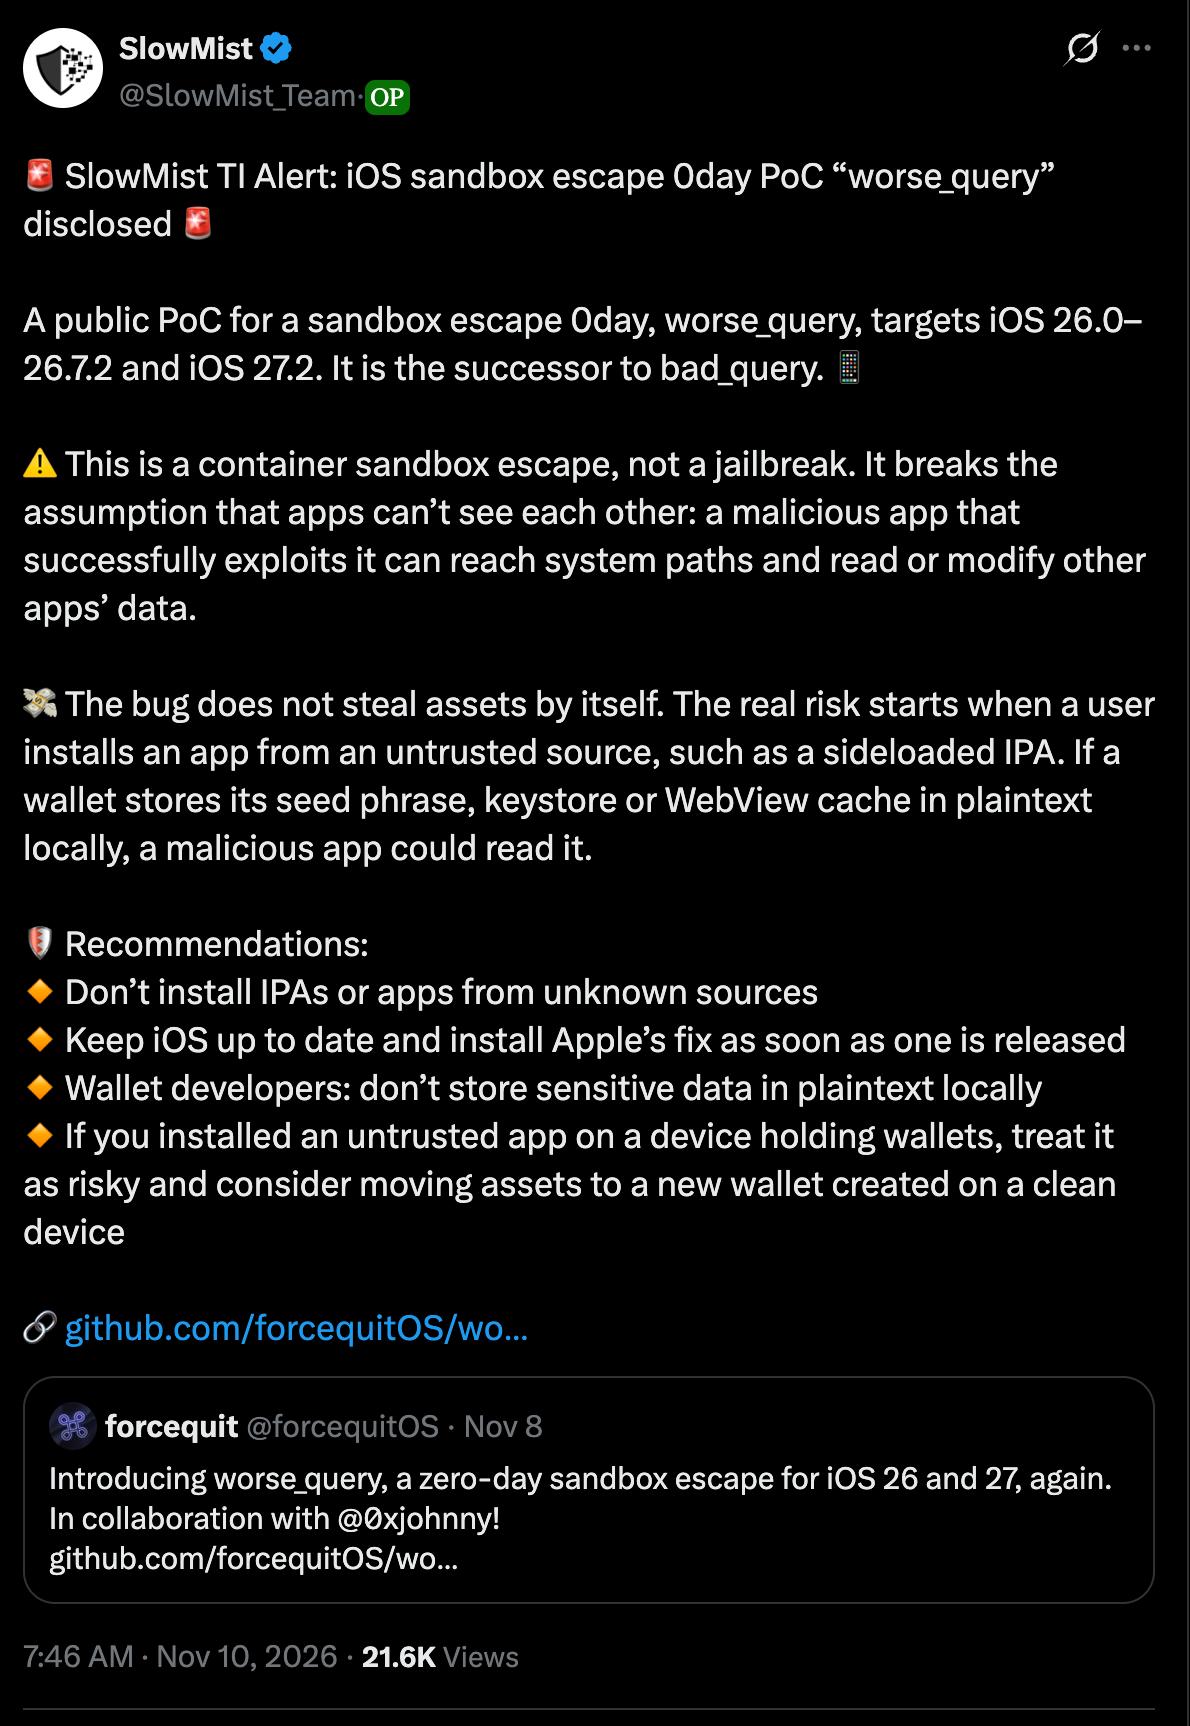
iOS sandbox escape 0day PoC “worse_query” disclosed, targets iOS 26.0–26.7.2 and iOS 27.2
𝕏/@SlowMist_Team •
Revision history
15 recorded changes
Want your article here?
Promote with Leviathan News15 recorded changes
Want your article here?
Promote with Leviathan NewsSlowMist's threat intelligence alert explains that worse_query is a container sandbox escape, not a jailbreak, allowing a malicious app to access system paths and read or modify other apps' data. The bug itself does not steal assets; risk arises with sideloaded IPAs, which could read plaintext seed phrases or keystore data. Separately, SlowMist reports an Ankr loss of roughly $304.5k after an attacker submitted five forged cross-chain receipts reusing one legitimate Optimism transaction, each with valid trusted-signer signatures; the origin of those signatures remains under investigation. SlowMist advises avoiding untrusted app sources, updating iOS, and moving wallet assets to a clean device if an untrusted app was installed.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Restoring your session before loading comments…
Related coverage is temporarily unavailable.