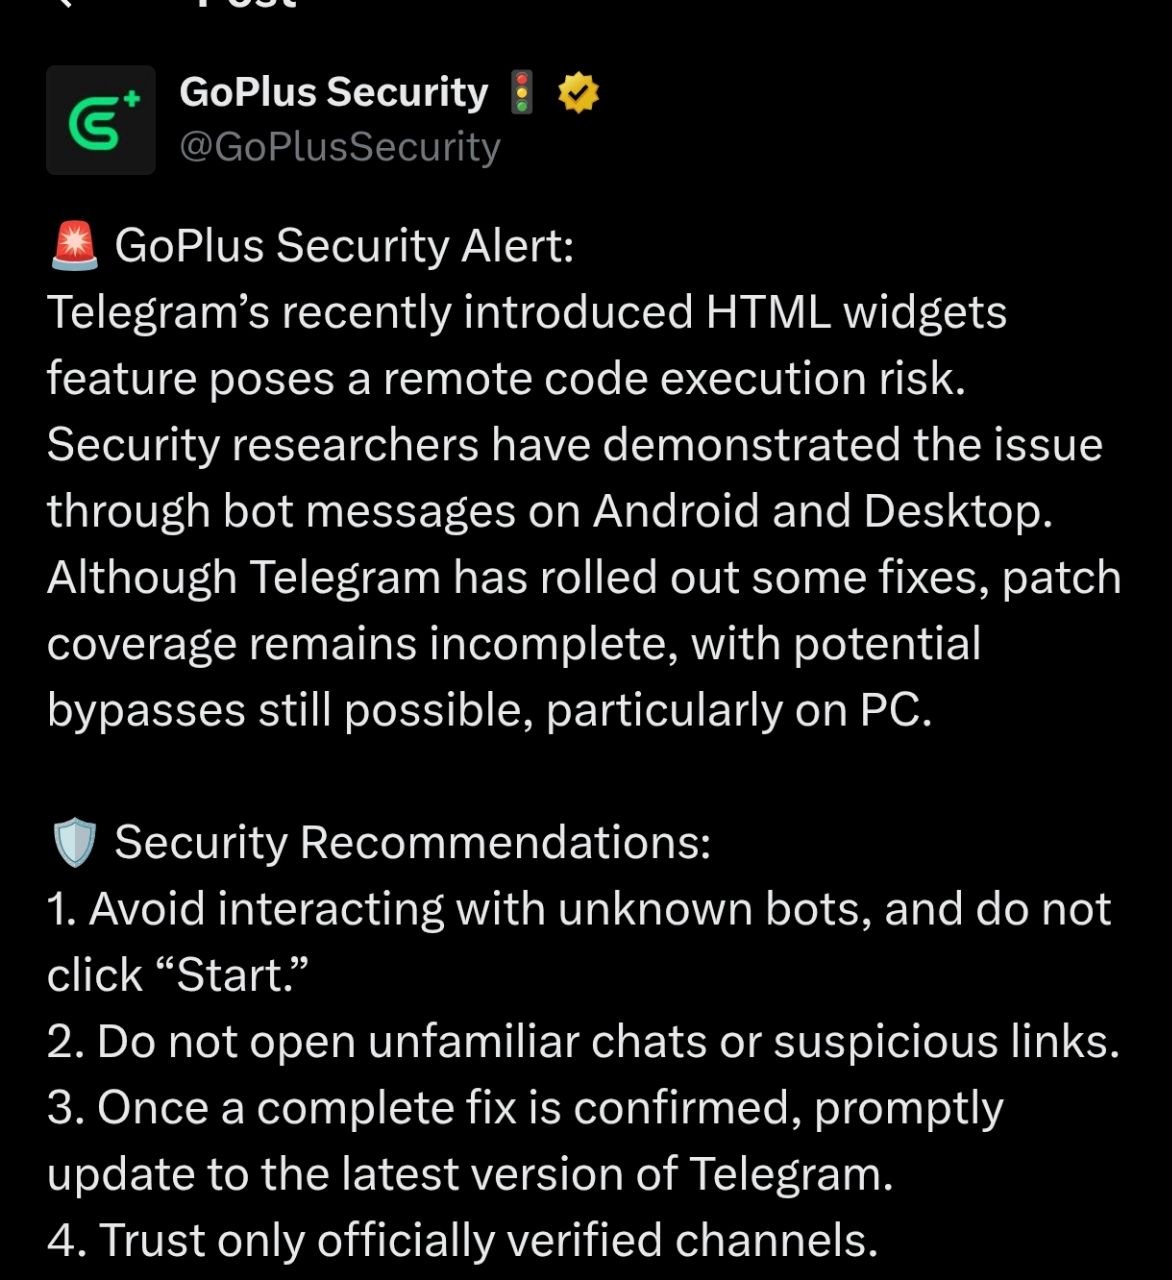
GoPlus warns Telegram HTML widgets pose remote code execution risk, with patch coverage incomplete
𝕏/@GoPlusSecurity •
Revision history
5 recorded changes
Want your article here?
Promote with Leviathan News5 recorded changes
Want your article here?
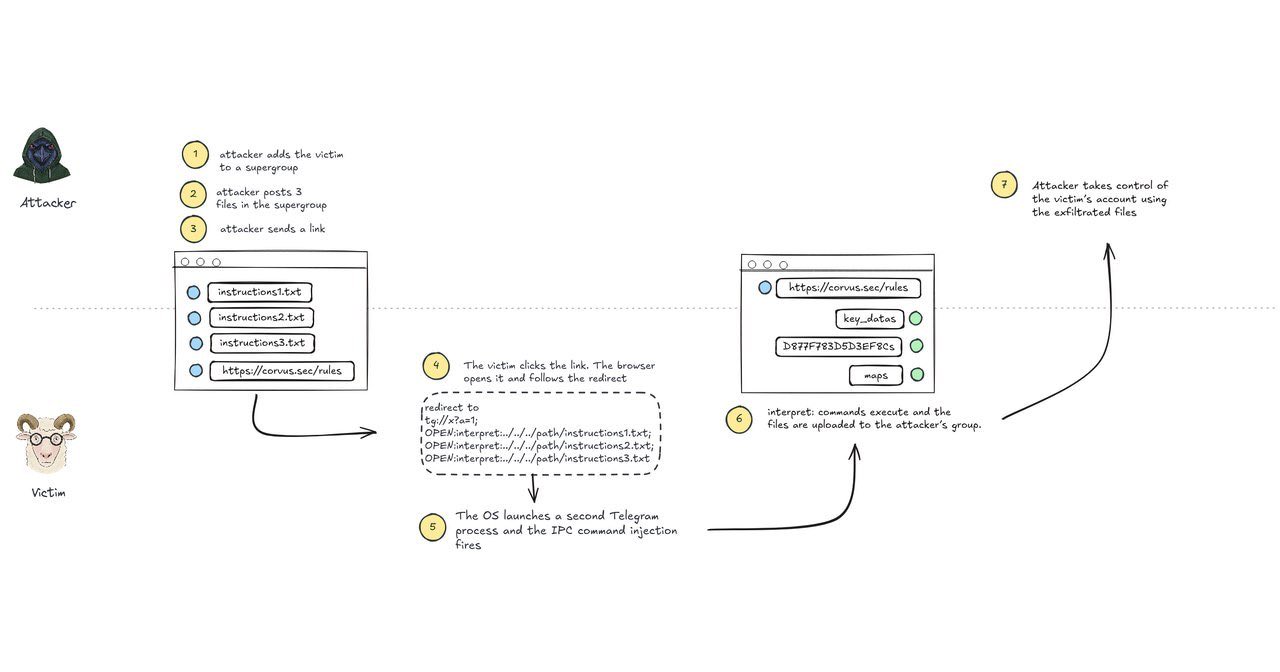
Promote with Leviathan NewsGoPlus Security reported that Telegram's HTML widgets feature carries a remote code execution risk, demonstrated through bot messages on Android and Desktop. Telegram has rolled out some fixes, but coverage remains incomplete, with potential bypasses still possible, particularly on PC. Researcher @v12sec showed an RCE working on the patched Windows client and said unsandboxed QuickJS in messages widens the attack surface. GoPlus instructs users to avoid unknown bots, not click "Start," and not open unfamiliar chats or suspicious links, trusting only verified channels. Once a complete fix is confirmed, users should update to the latest Telegram version, GoPlus said.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Restoring your session before loading comments…
The Block ·
𝕏/@josephfcox ·
𝕏/@AlchemyPay ·
404media.co ·
ꘜ/@SquidDAOalert ·
𝕏/@officer_secret ·
The Block ·
𝕏/@josephfcox ·
𝕏/@AlchemyPay ·
404media.co ·
ꘜ/@SquidDAOalert ·
𝕏/@officer_secret ·