A user of VenusProtocol has been drained ~$27M in crypto after falling for a phishing scam.
The victim approved a malicious transaction, granting token approval to the attacker's address (0x7fd8...202a) for asset transfer.
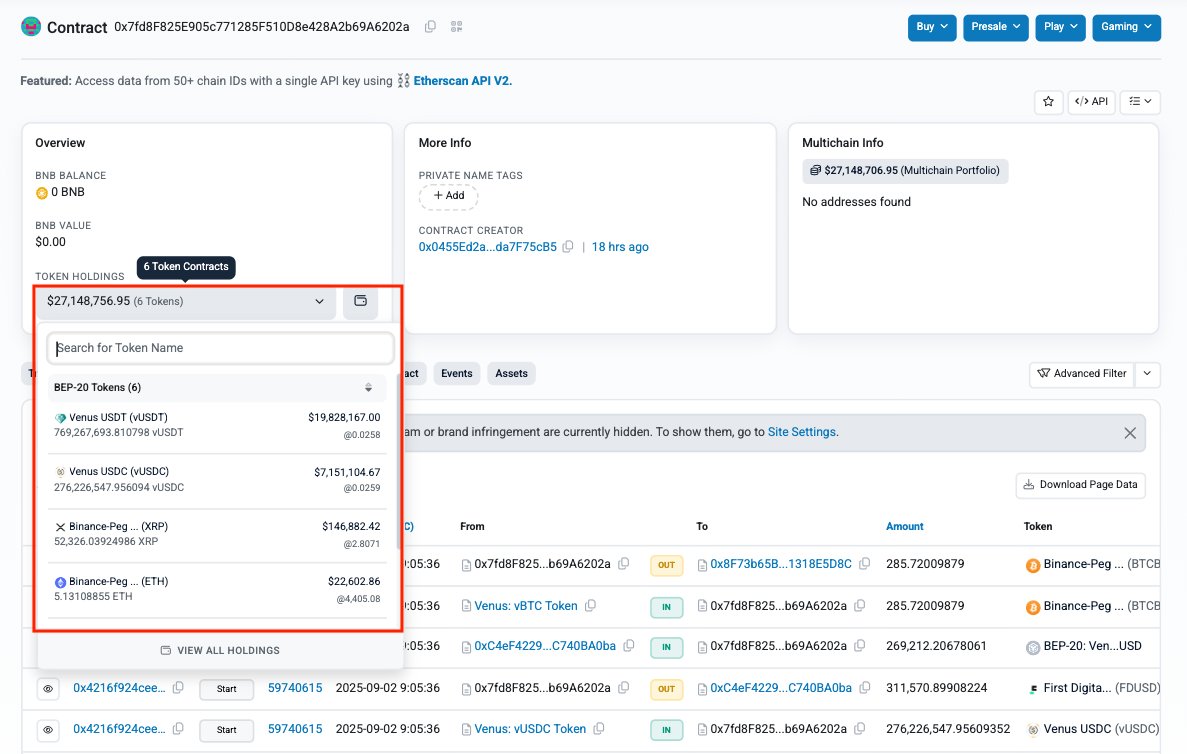
𝕏/@PeckShieldAlert •
Revision history
8 recorded changes
Want your article here?
Promote with Leviathan News