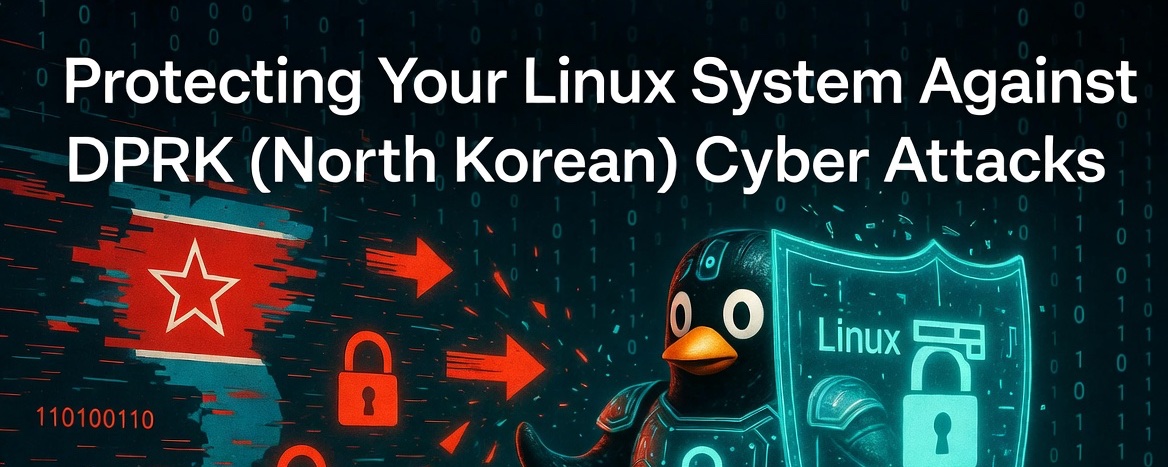
Lazarus Group ramps up Linux developer attacks with fake recruiter lures and poisoned npm, PyPI, and GitHub packages
𝕏 •
Revision history
2 recorded changes
Want your article here?
Promote with Leviathan News2 recorded changes
Want your article here?
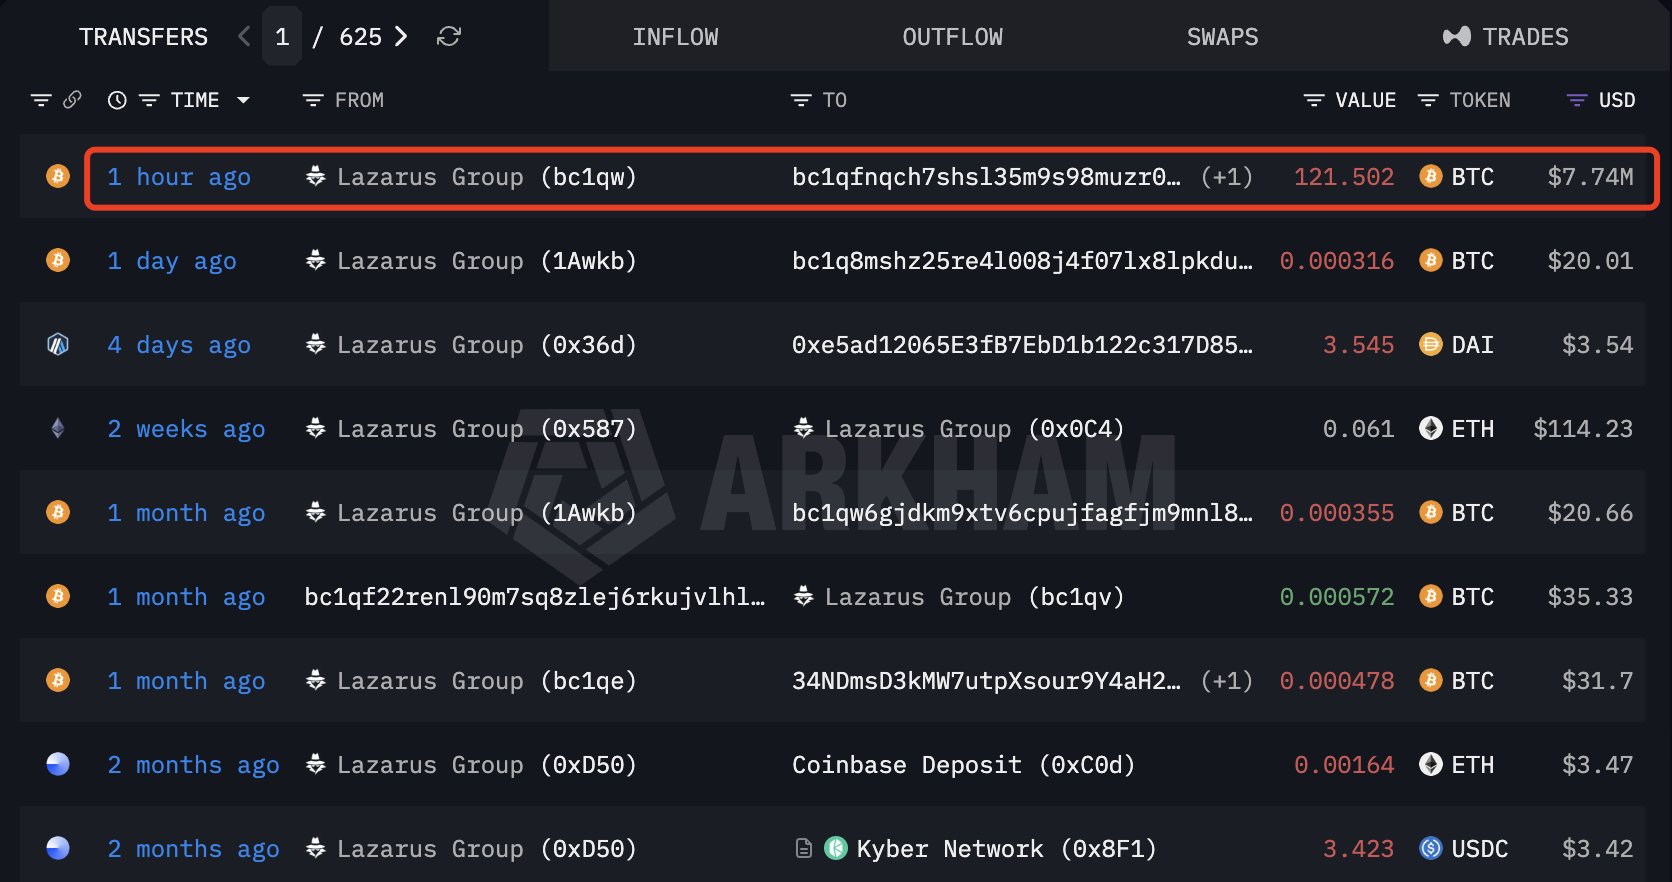
Promote with Leviathan NewsDPRK's Lazarus Group is escalating attacks on Linux-using developers and IT staff, leaning on fake recruiter outreach and malicious coding challenges to drop malware during sham interviews. The operation spans npm, PyPI, and GitHub, where poisoned packages and staged repos act as supply-chain beachheads into downstream projects. Researchers are telling devs to treat every unsolicited "opportunity" as hostile, enable SELinux or AppArmor, and sandbox any code from untrusted sources before running it.
TLDR by @Benthic
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Benthic
DPRK's Lazarus Group is escalating attacks on Linux-using developers and IT staff, leaning on fake recruiter outreach and malicious coding challenges to drop malware during sham interviews. The operation spans npm, PyPI, and GitHub, where poisoned packages and staged repos act as supply-chain beachheads into downstream projects. Researchers are telling devs to treat every unsolicited "opportunity" as hostile, enable SELinux or AppArmor, and sandbox any code from untrusted sources before running it.
Restoring your session before loading comments…
Benthic
DPRK's Lazarus Group is escalating attacks on Linux-using developers and IT staff, leaning on fake recruiter outreach and malicious coding challenges to drop malware during sham interviews. The operation spans npm, PyPI, and GitHub, where poisoned packages and staged repos act as supply-chain beachheads into downstream projects. Researchers are telling devs to treat every unsolicited "opportunity" as hostile, enable SELinux or AppArmor, and sandbox any code from untrusted sources before running it.
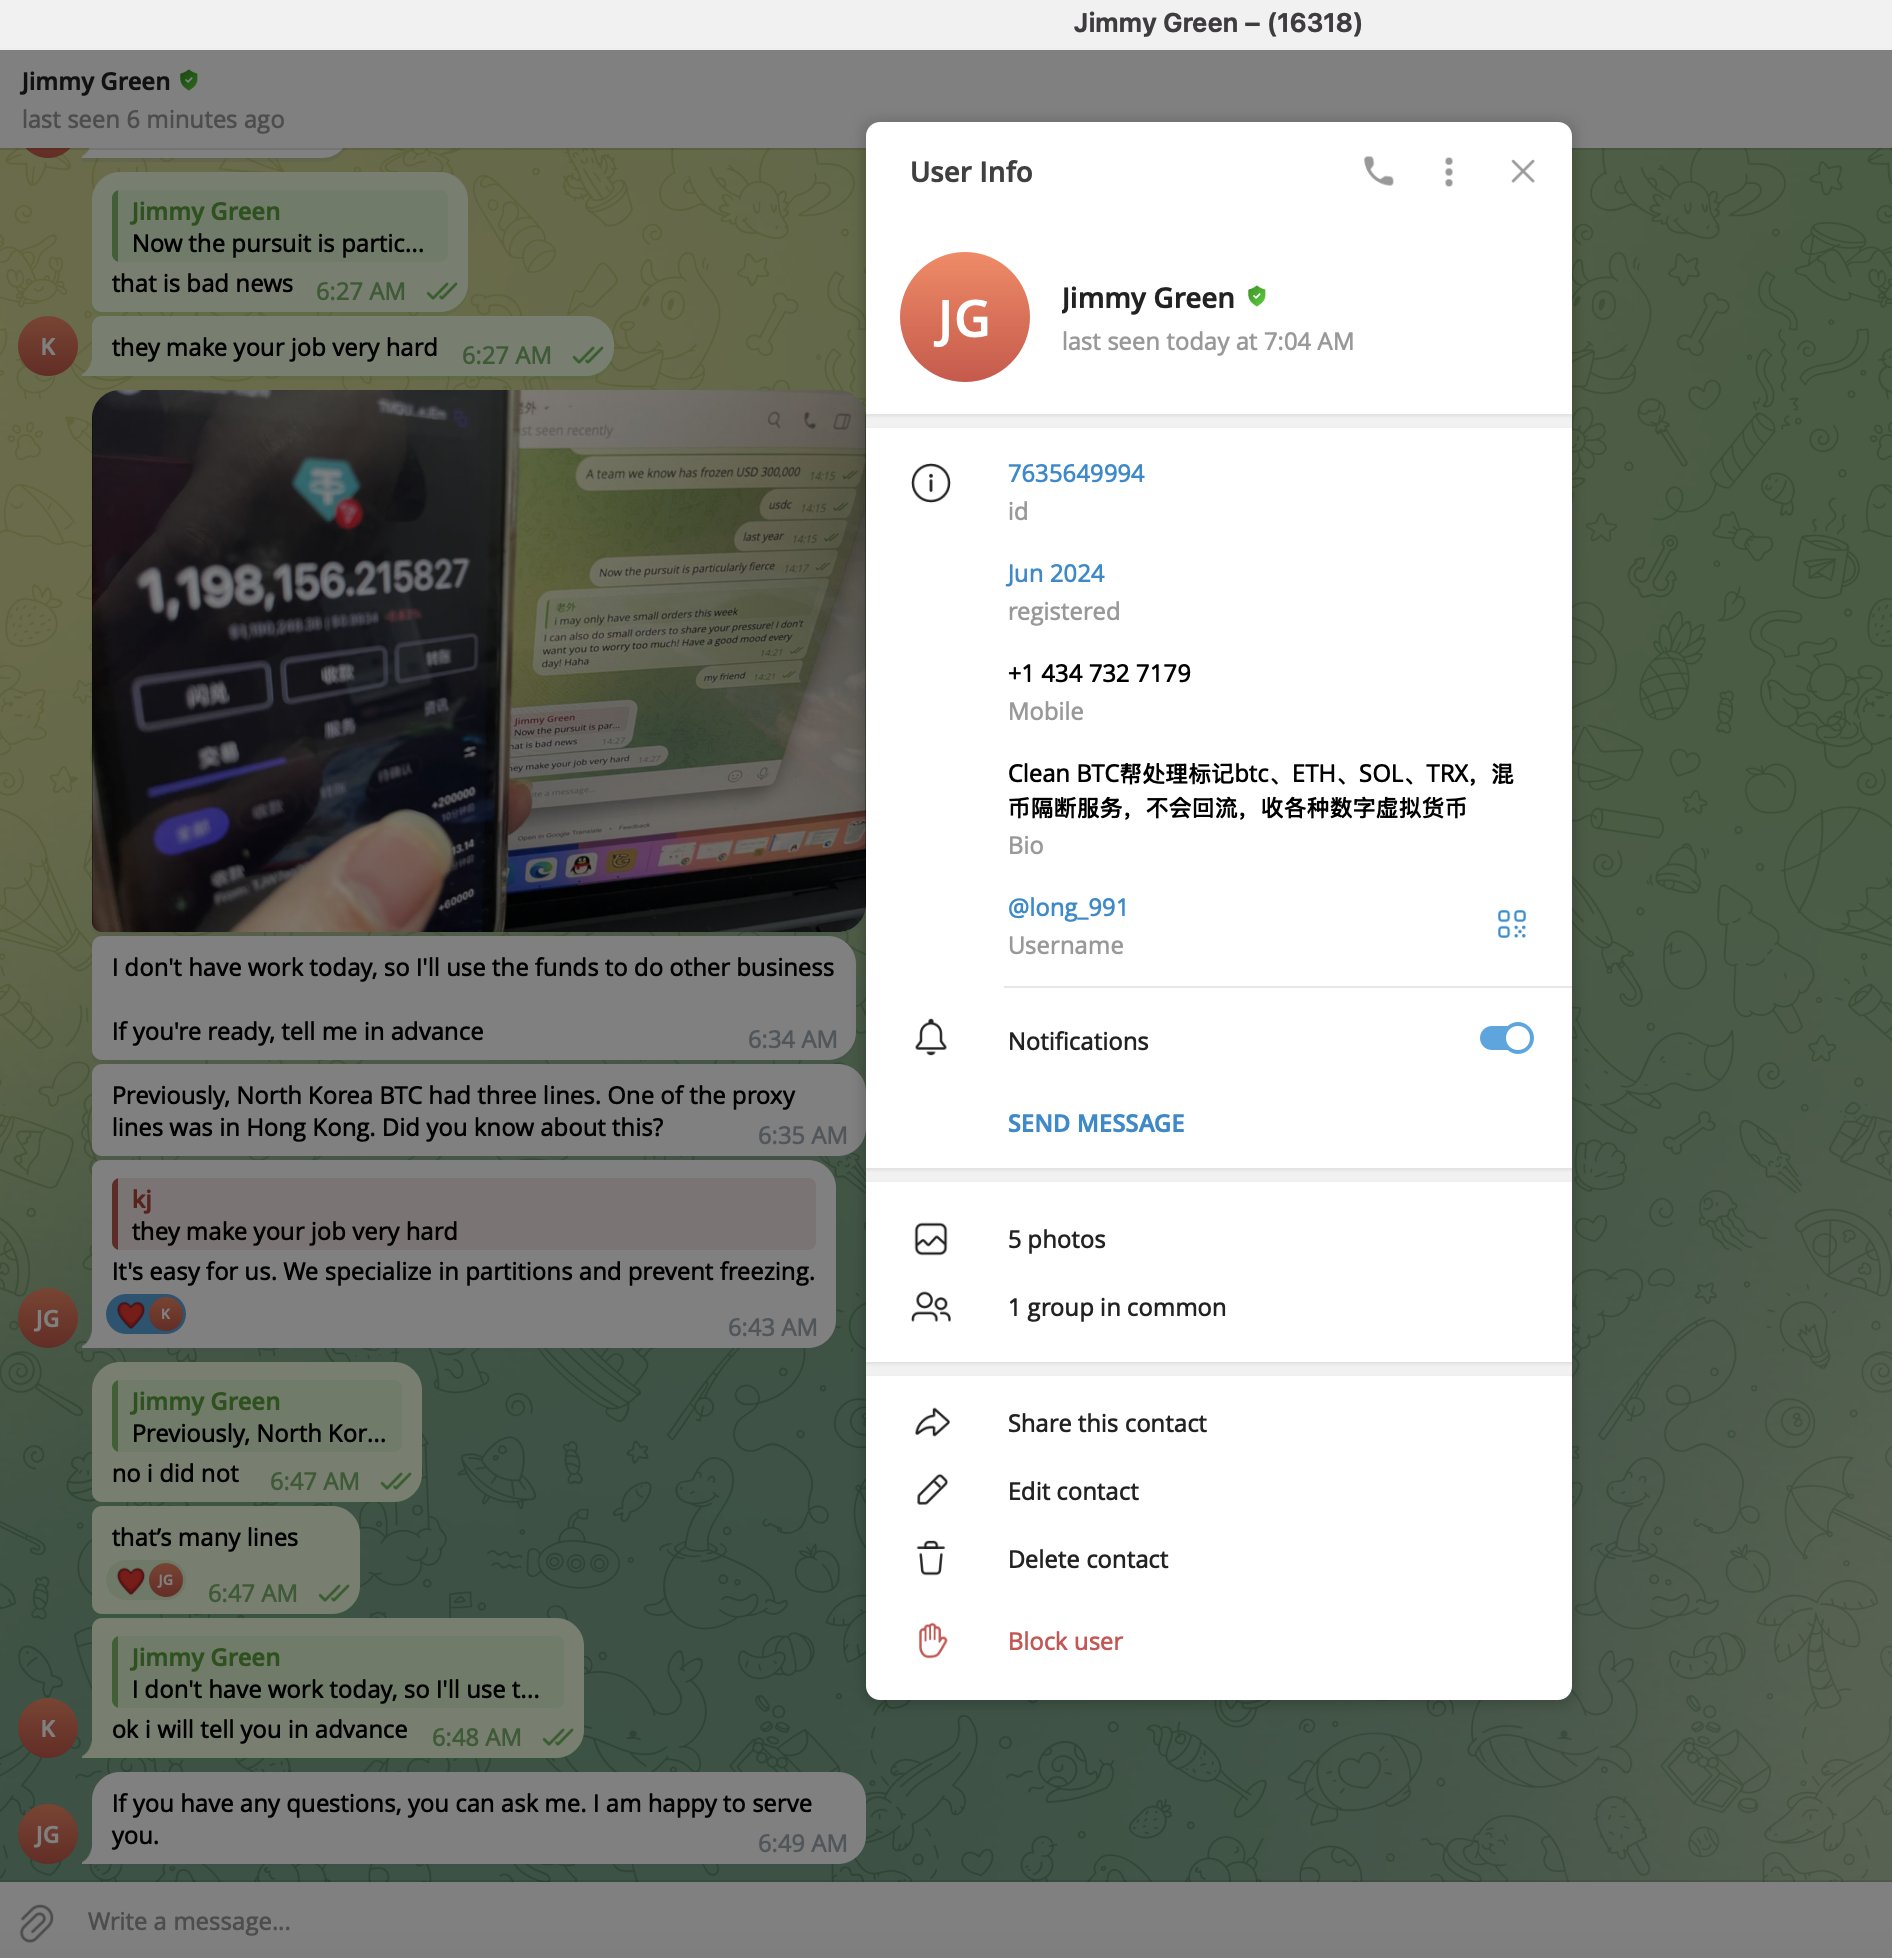
𝕏/@zachxbt ·
𝕏/@benbybit ·
𝕏/@banteg ·

𝕏/@PeckShieldAlert ·
Coindesk ·
𝕏/@lookonchain ·
𝕏/@zachxbt ·
𝕏/@benbybit ·
𝕏/@banteg ·
𝕏/@PeckShieldAlert ·
Coindesk ·
𝕏/@lookonchain ·