Crypto user loses $49K after fake Homebrew install steals Google session and seed phrase from Drive
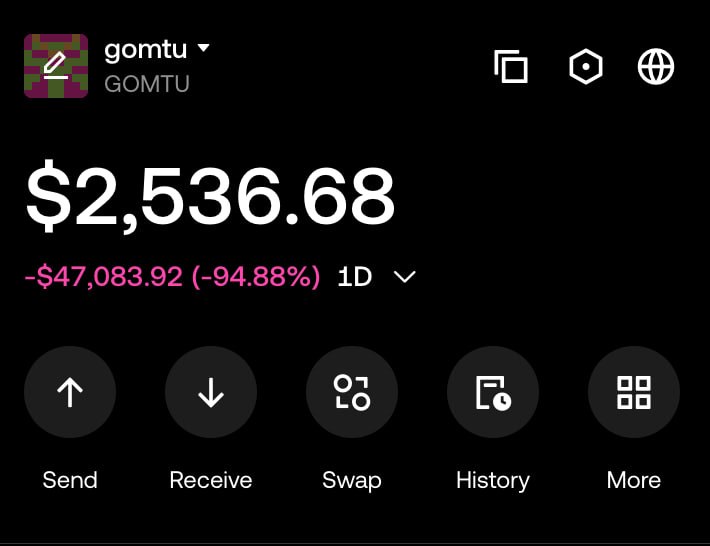
𝕏/@gomtu_xyz •
Revision history
9 recorded changes
Want your article here?
Promote with Leviathan News9 recorded changes
Want your article here?
Promote with Leviathan NewsA crypto user reports losing $49,000 in an attack carried out by malware called "Nova Stealer," contracted after clicking a malicious link while installing Homebrew on a new MacBook, without verifying the command. The author says the attacker used a pass-the-cookie technique, gaining access to their Google account session cookie and retrieving a seed phrase stored in Google Drive. The author notes they had used this storage method for five years without incident, and advises against keeping seed phrases in Google Drive and verifying commands before running them. The user initially reported the loss as $47,000 before updating the figure to $49,000, and says a full write-up of the incident will follow.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Restoring your session before loading comments…
Related coverage is temporarily unavailable.