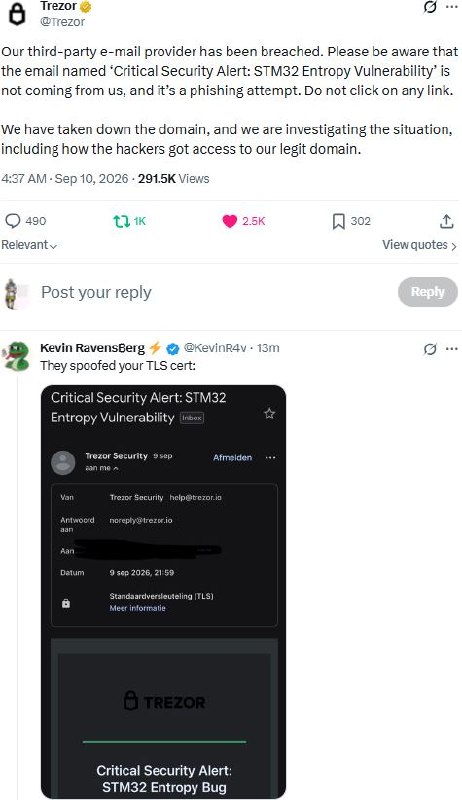
Trezor email provider breach triggers phishing alert; hardware wallet firm shuts down domain
𝕏/@Trezor •
Revision history
7 recorded changes
Want your article here?
Promote with Leviathan News7 recorded changes
Want your article here?
Promote with Leviathan NewsTrezor says the breach affected its third-party email provider, not the company's own systems directly. A phishing email titled 'Critical Security Alert: STM32 Entropy Vulnerability' is circulating; Trezor confirms it did not send the message and urges recipients not to click any links in it. The company states it has taken down the compromised domain and is investigating, including how attackers obtained access to its legitimate domain. No further details on the incident's scope or timing were provided.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Restoring your session before loading comments…
Related coverage is temporarily unavailable.