MEV bot front-runs $7.81M rsETH exploit, leaving Gnosis Safe whale with $7.73M loss
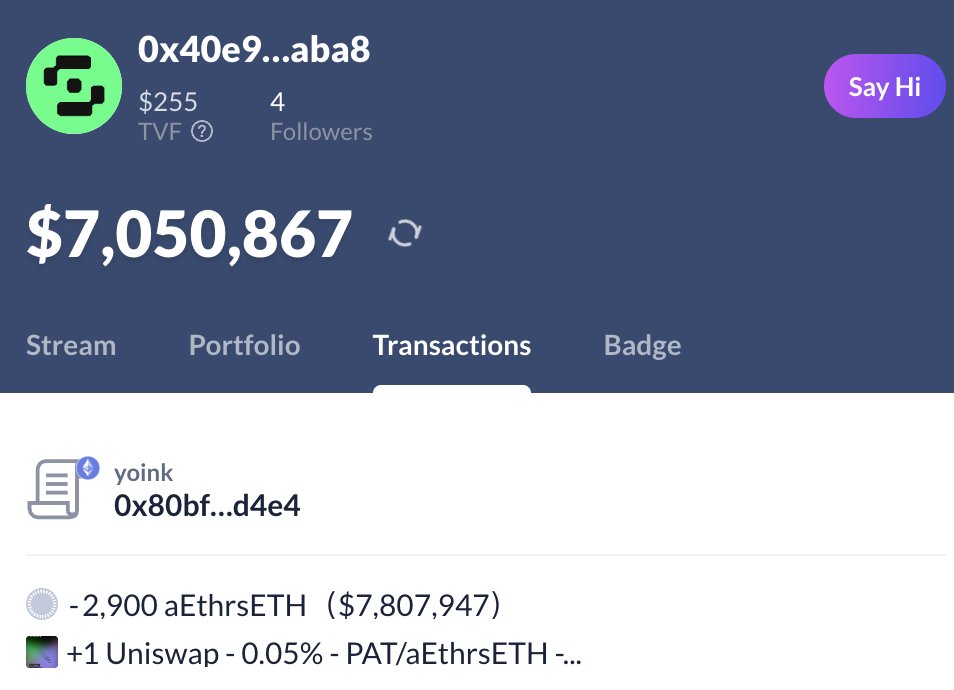
𝕏/@DefimonAlerts •
Revision history
4 recorded changes
Want your article here?
Promote with Leviathan News4 recorded changes
Want your article here?
Promote with Leviathan NewsAn MEV bot called "yoink" front-ran the exploit in the mempool, capturing the entire ~$7.8M for itself before the original attacker's transaction landed. The attacker had deployed a "Permissionless Attacker Token" to launch the attack. Per the author, the root cause was a whitelisted Safe module acting as strategy executor for whale 0x40E9's leveraged rsETH funds. The module forwarded caller-supplied calldata to execTransactionFromModuleReturnData with DELEGATECALL and no caller gating, letting anyone execute arbitrary code in the Safe's context. The whale reportedly lost $7.73M.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Loading comments…
Restoring your session before loading comments…
𝕏/@blocmates ·
𝕏/@WhiteWhaleLabs ·
𝕏/@_PLabs ·
𝕏/@JupiterExchange ·

𝕏/@officer_secret ·
The Block ·
𝕏/@blocmates ·
𝕏/@WhiteWhaleLabs ·
𝕏/@_PLabs ·
𝕏/@JupiterExchange ·
𝕏/@officer_secret ·
The Block ·