Payy’s post-mortem details $1.83M USDC exploit involving an invalid burn proof accepted by its Noir/Barretenberg verifier
𝕏/@payy_link •
Revision history
5 recorded changes
Want your article here?
Promote with Leviathan News5 recorded changes
Want your article here?
Promote with Leviathan NewsPayy's post-mortem attributes the September 24, 2026 exploit to a proving-system vulnerability in the Noir/Barretenberg verifier developed by Aztec, which accepted an invalid burn proof submitted by an attacker. The first burn released 1,828,589.378132 USDC from the Payy rollup despite the transaction appearing invalid. A second 1 USDC burn was paid early by a burn substitutor and later reimbursed, releasing a further 90,202.820016 USDC to the same receiving wallet. All Payy Network transactions, including deposits, withdrawals, transfers and card transactions, were paused during the investigation.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
𝕏/@PirateChain ·
𝕏/@fatmanterra ·
ꘜ/@thatsrekt_alerts ·
𝕏/@blockaid_ ·
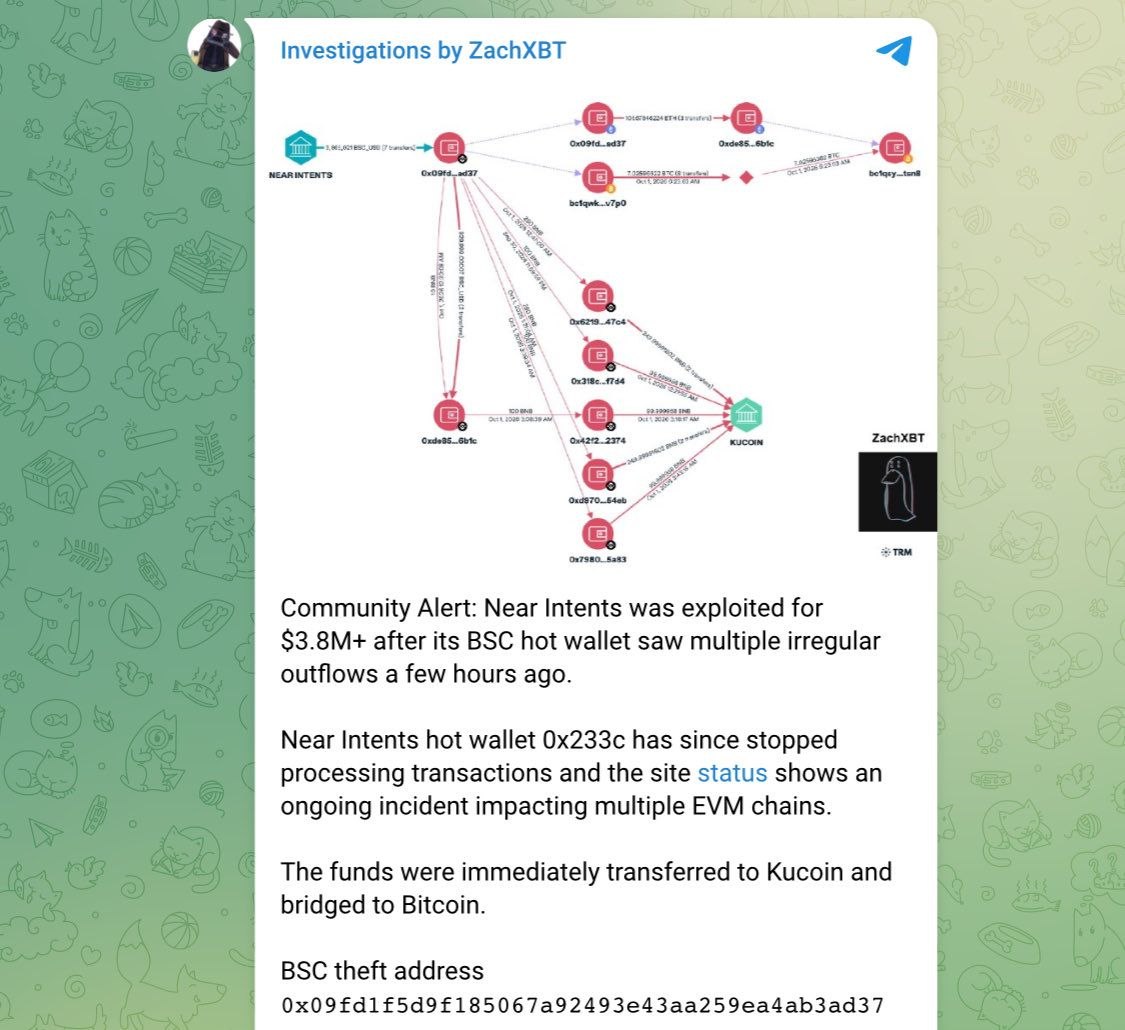
𝕏/@near_intents ·
ꘜ/@investigations ·
𝕏/@PirateChain ·
𝕏/@fatmanterra ·
ꘜ/@thatsrekt_alerts ·
𝕏/@blockaid_ ·
𝕏/@near_intents ·
ꘜ/@investigations ·
Restoring your session before loading comments…