SlowMist links Bitget hot wallet theft to zero-day exploit and fake withdrawal tool
𝕏/@SlowMist_Team •
Revision history
7 recorded changes
Want your article here?
Promote with Leviathan News7 recorded changes
Want your article here?
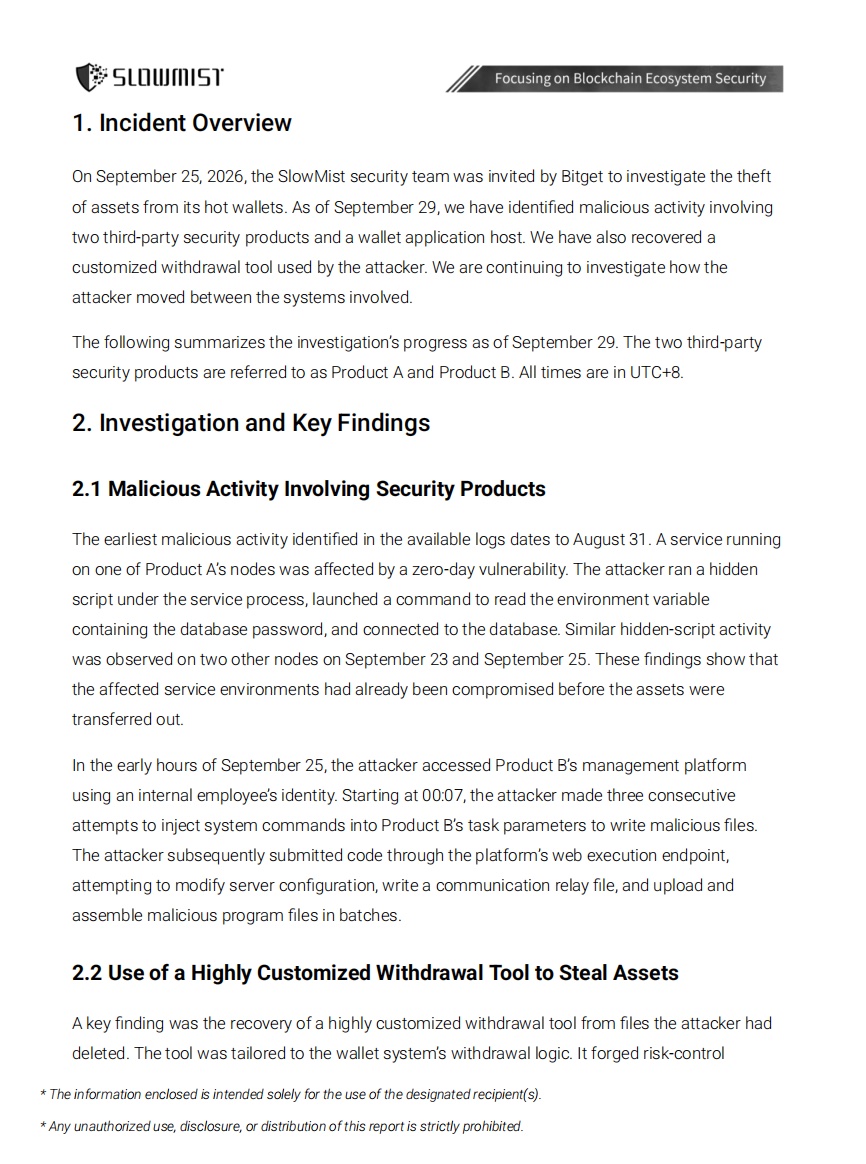
Promote with Leviathan NewsSlowMist, engaged by Bitget, reports that the September 25 hot wallet theft involved a zero-day vulnerability in a third-party security product. The attacker used an internal employee identity to access a third-party management platform on September 25 and deployed a customized withdrawal tool interacting with the wallet system's withdrawal logic. On-chain movement began at 02:25 UTC+8 and spanned roughly 2 hours 52 minutes across multiple blockchains, followed by attempts to manipulate withdrawal records and trigger further BTC withdrawals. How the attacker moved between systems remains under investigation.
AI summary of the linked source — not editorial content.
10 reports
first post
Leviathan +4.1 h later
All times UTC.
@bitget has engaged SlowMist’s security team to investigate the September 25 hot wallet asset theft. As of September 29, our investigation has identified malicious activity involving certain third-party security products and a wallet application host, as well as a highly…
We are very grateful for SlowMist's quick response and professionalism in helping us investigate this incident thoroughly. They have shared their findings on the September 24 security incident. Their investigation identified malicious activity involving third-party security… https://t.co/tlAGAkIMJn
慢雾披露 Bitget 调查进展:攻击者伪造风控参数提币 针对 Bitget 此前披露的约 3.875 亿美元安全事件,慢雾发布调查进展报告,梳理了第三方安全产品遭入侵、定制工具提币及后续 BTC 提币尝试等发现。 主要发现如下,时间均为北京时间: 1.最早的入侵痕迹可追溯至 8 月 31 日。 第三方安全产品 A… https://t.co/f6Vn5bpdBN
it's very easy to see here. $ZEC is NOT private. $XMR is. That's why they ban one and not the other. https://t.co/y1rKQCwXob
I'm starting to think $ZEC is useless as a privacy token. Not only did Bitget hacker get identified easily (with no real info on HOW), they're now tracing the swaps through Tornado Cash INTO SHIELDED ZEC. Still sticking with $XMR. https://t.co/RzfWRA4IRT
so if $ZEC hacked funds can be traced, that makes $XMR the real privacy btc right
32 more accounts posted about this · 2 Telegram channels (no public link)
Social-monitoring data, not investment advice Elfa post text from Xas of
Loading related coverage…
Loading comments…
𝕏/@PirateChain ·
𝕏/@fatmanterra ·
ꘜ/@thatsrekt_alerts ·
𝕏/@blockaid_ ·
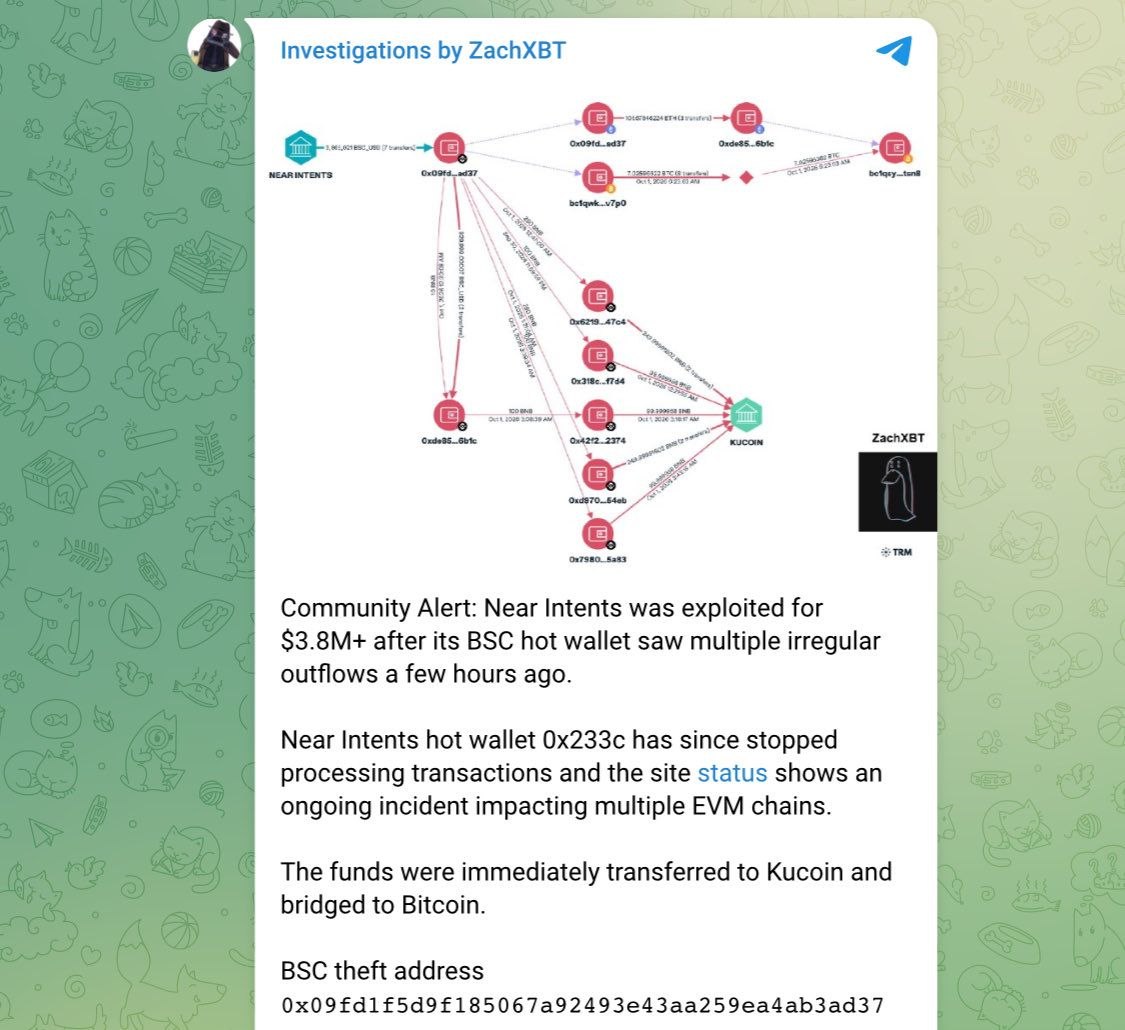
𝕏/@near_intents ·
ꘜ/@investigations ·
𝕏/@PirateChain ·
𝕏/@fatmanterra ·
ꘜ/@thatsrekt_alerts ·
𝕏/@blockaid_ ·
𝕏/@near_intents ·
ꘜ/@investigations ·
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Loading comments…
Restoring your session before loading comments…