Red-teaming Bitcoin's elliptic curve: five open math questions that would need solving to break secp256k1
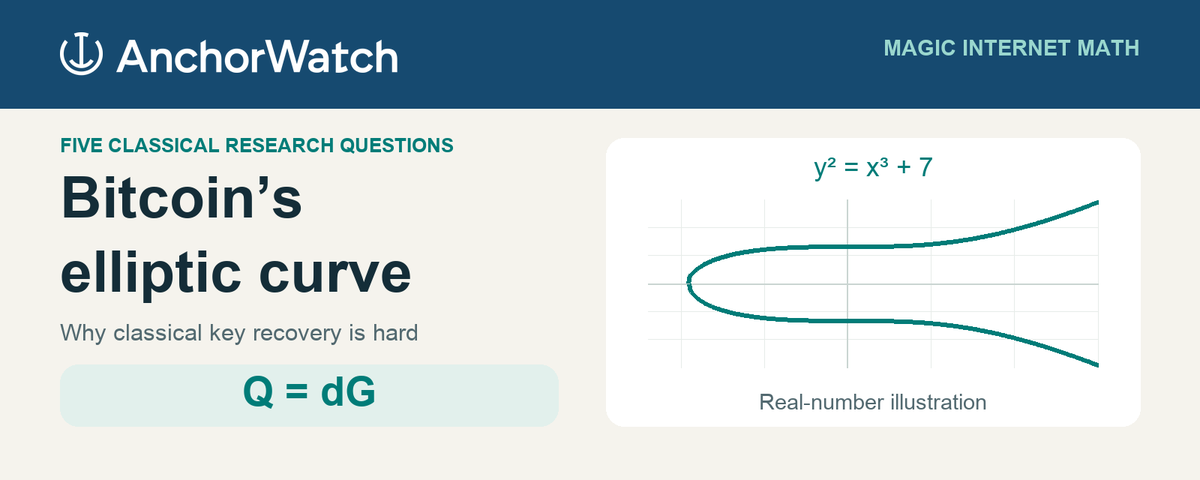
𝕏/@Rob1Ham •
Revision history
5 recorded changes
Want your article here?
Promote with Leviathan News5 recorded changes
Want your article here?
Promote with Leviathan NewsRob1ham and Fundamentals21m red-teamed elliptic-curve cryptography on the Magic Internet Math podcast, arguing that vague claims about math breaking Bitcoin skip the specific open problems. The author, who holds a math bachelor's but is not a cryptographer, lists five questions: cheap point relations via Semaev summation polynomials; findable small minors from the initial-minors conjecture; non-generic algorithms beating Shoup's generic square-root bound; secp256k1's j-invariant 0 endomorphism or an isogenous cousin curve; and lifting to characteristic zero. The usual classical estimate is roughly 2^128 group operations.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
reports.tiger-research ·
WSJ ·
Tradingview ·
𝕏/@ztownsend ·
𝕏/@dreaming ·
babylonlabs.io ·
reports.tiger-research ·
WSJ ·
Tradingview ·
𝕏/@ztownsend ·
𝕏/@dreaming ·
babylonlabs.io ·
Loading comments…
Restoring your session before loading comments…