NEAR Intents recovers $3.8M after contract bug minted ghost funds, removes flawed feature
𝕏/@AlexAuroraDev •
Revision history
4 recorded changes
Want your article here?
Promote with Leviathan News4 recorded changes
Want your article here?
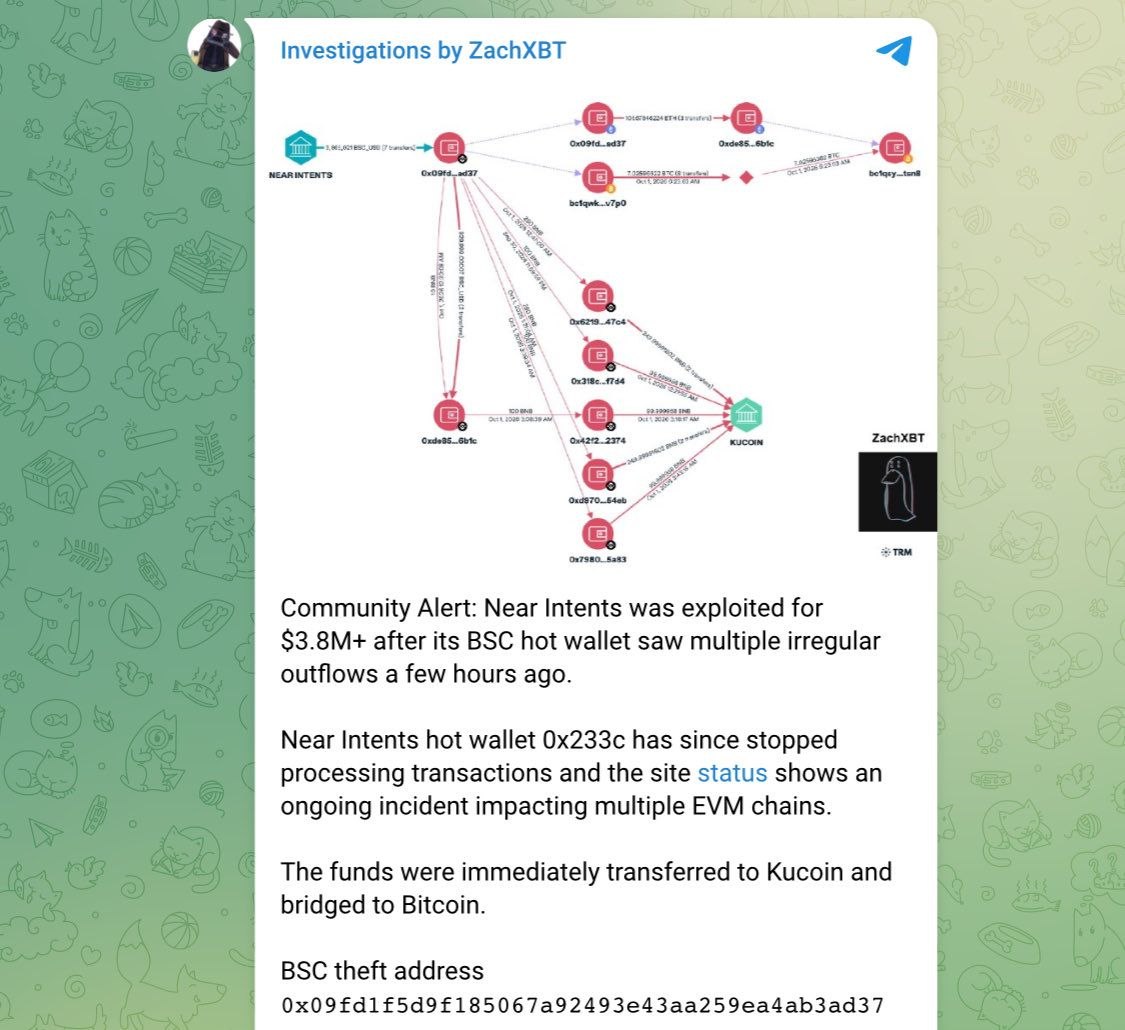
Promote with Leviathan NewsA bug in NEAR Intents' deposit notification feature let an attacker exploit failed third-party contract calls, minting $3.8M in ghost funds across 23 transactions before withdrawing via Omni. The flaw arose because the token contract refunded deposits while NEAR Intents kept records, letting the attacker legitimately bridge funds out between Sept 29 and Oct 1. All funds were recovered within 36 hours after negotiations with the attacker. The team removed the notification feature, added automatic invariant monitoring that pauses the contract, and awarded $300k for a related bug bounty report.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
Restoring your session before loading comments…
𝕏/@NEARProtocol ·
𝕏/@near_intents ·
The Block ·
𝕏/@NEARProtocol ·
𝕏/@NEARProtocol ·
𝕏/@ShieldFi ·
𝕏/@NEARProtocol ·
𝕏/@near_intents ·
The Block ·
𝕏/@NEARProtocol ·
𝕏/@NEARProtocol ·
𝕏/@ShieldFi ·