Security guide urges phishing-resistant MFA after Binance's $6.34B theft and PHP2Shell flaw
𝕏/@jackhcable •
Revision history
6 recorded changes
Want your article here?
Promote with Leviathan News6 recorded changes
Want your article here?
Promote with Leviathan NewsJack Cable's security guide argues that recent incidents stem from long-known weaknesses, not novel techniques. The Binance theft began with malware from a fake job interview and tampered installer, exposing a deployment token that reached the wallet signing service. Other events include the PHP2Shell flaw affecting roughly 70% of websites, a malicious Claude Code Cursor extension installed by fewer than 5,000 users, and eMudhra's certificate authority using the number 4 as its private key. Recommended immediate steps include phishing-resistant MFA, secret scanning, and 7-day package age minimums.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
𝕏/@exvulsec ·
𝕏/@Grayscale ·
Binance ·
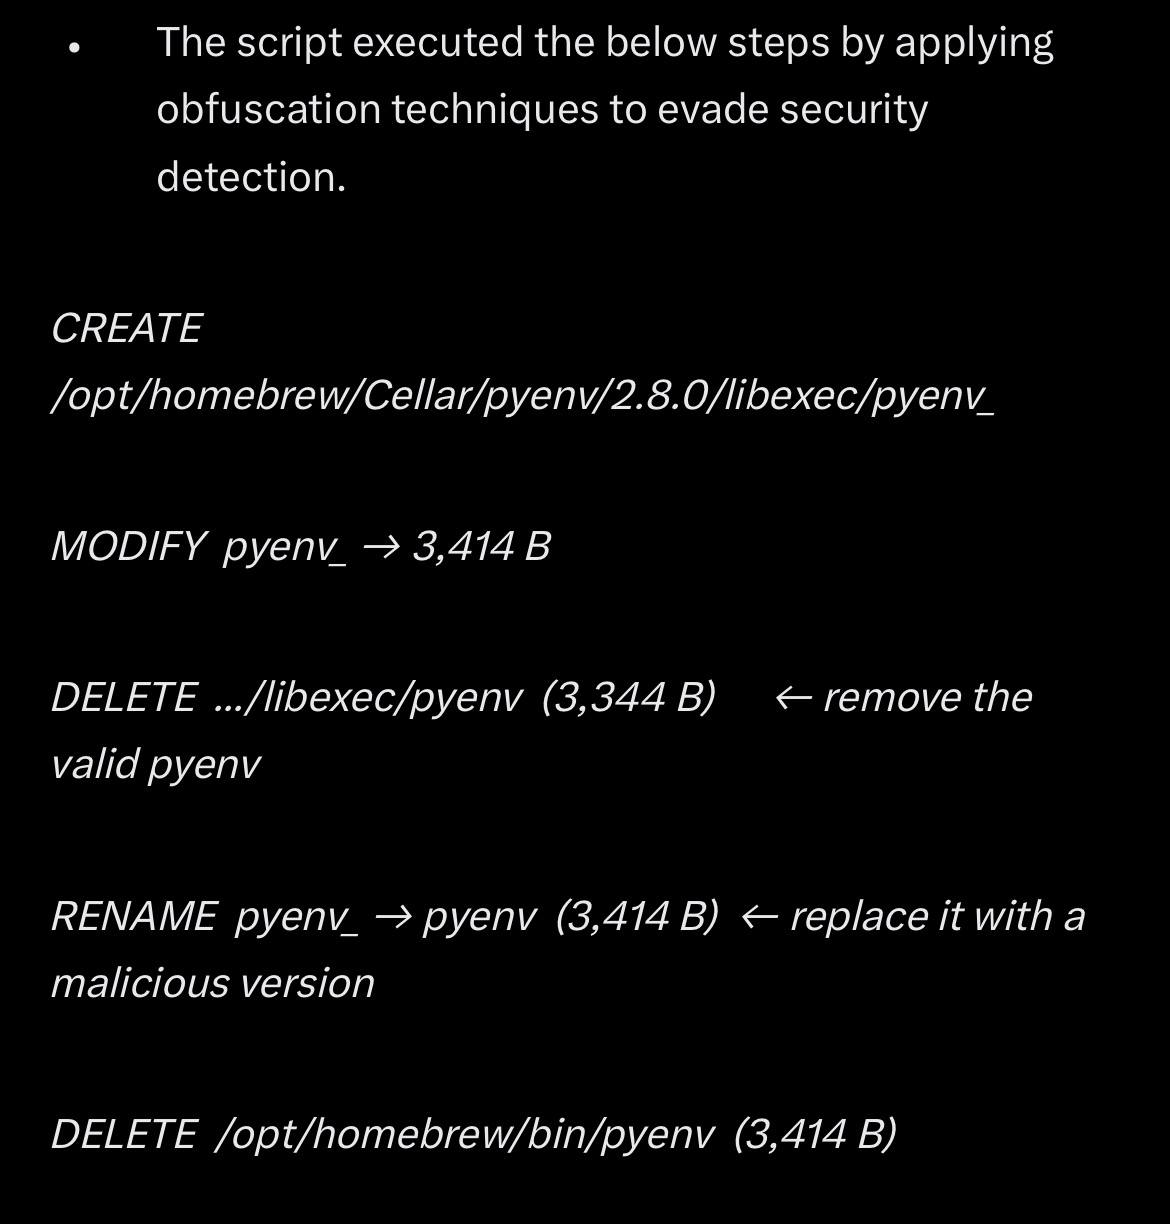
𝕏/@binance ·
𝕏/@binance ·
𝕏/@FBIJacksonville ·
𝕏/@exvulsec ·
𝕏/@Grayscale ·
Binance ·
𝕏/@binance ·
𝕏/@binance ·
𝕏/@FBIJacksonville ·
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Restoring your session before loading comments…