OSK CoreVault on BNB Chain loses ~$175K in exploit tied to oracle pricing flaw
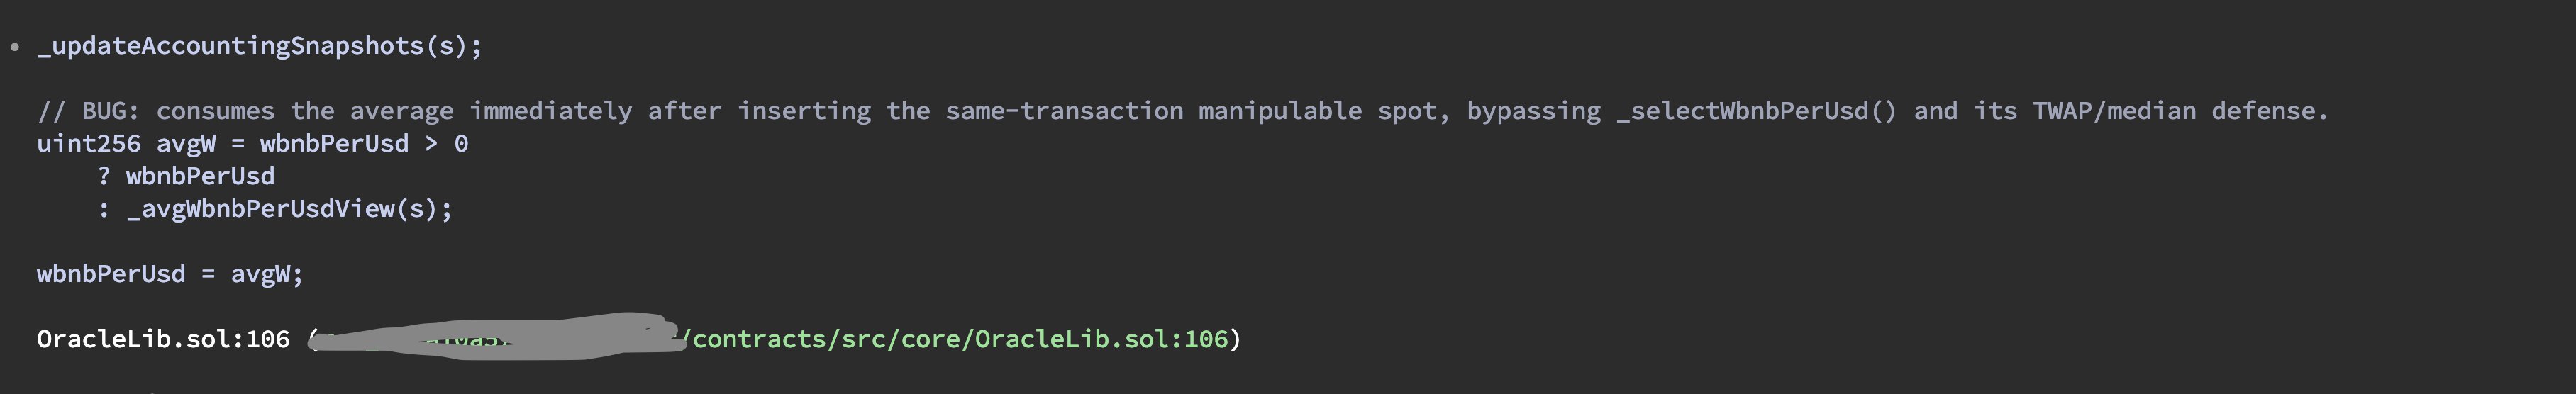
𝕏/@exvulsec •
Revision history
4 recorded changes
Want your article here?
Promote with Leviathan News4 recorded changes
Want your article here?
Promote with Leviathan NewsThe exploit stemmed from a pricing flaw in CoreVaultFarming._redeemPrincipalCore(), which settles via OracleLib.getAccountingPrices(). That function pushes the same-transaction Pancake WBNB/USDT spot price into a 3-sample window and returns the raw average, never invoking the library's spot/TWAP/average median selector. Net losses reached ~251.23 BNB (~$175K). The attacker seeded an 8-BNB position, flash-borrowed 207,358.41 WBNB, and retained ~152.26 BNB. The report urges the InsurancePool owner to sever the vulnerable Treasury and evacuate remaining reserves.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
𝕏/@b14g_network ·
𝕏/@ProtocolTalis ·
𝕏/@zerolore ·
𝕏/@Coredao_Org ·
wublockchain.xyz ·
wublockchain.xyz ·
𝕏/@b14g_network ·
𝕏/@ProtocolTalis ·
𝕏/@zerolore ·
𝕏/@Coredao_Org ·
wublockchain.xyz ·
wublockchain.xyz ·
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Restoring your session before loading comments…