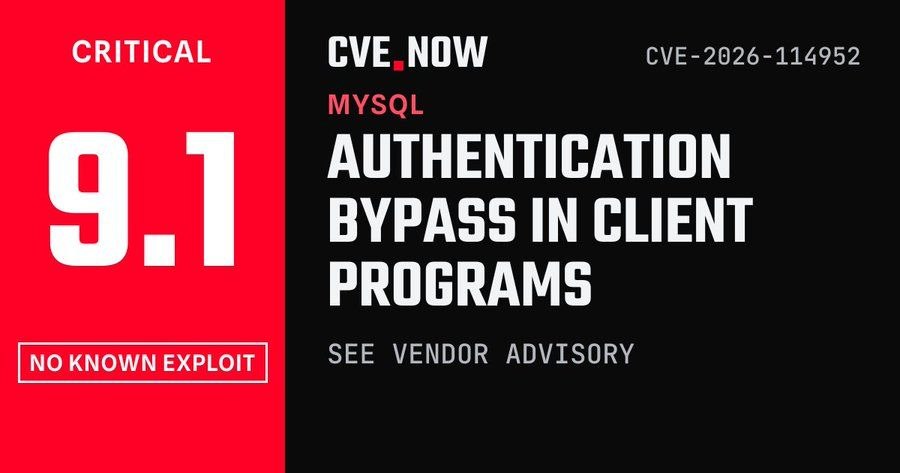
SlowMist warns of critical MySQL vulnerability with CVSS 9.1 that allows unauthenticated attackers to access and modify sensitive data.
𝕏/@SlowMist_Team •
Revision history
5 recorded changes
Want your article here?
Promote with Leviathan News5 recorded changes
Want your article here?
Promote with Leviathan NewsSlowMist's alert also reported a roughly $3.43M loss at k3_capital. The sBOLD vault checked how much BOLD a swap returned but failed to verify the router spent the same token and amount, so attackers left WETH in the vault while redeeming shares at a valuation that included it. They recovered the WETH through a second swap priced against 1 wei of wstETH, using an unused WETH approval, and extracted existing depositors' BOLD. SlowMist lists the attacker and vulnerable contract addresses. Separately, it urges MySQL users on the listed versions to patch CVE-2026-114952.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Loading comments…
Restoring your session before loading comments…
near.ai ·
𝕏/@Cloudflare ·
𝕏/@initia ·
𝕏/@claudeai ·
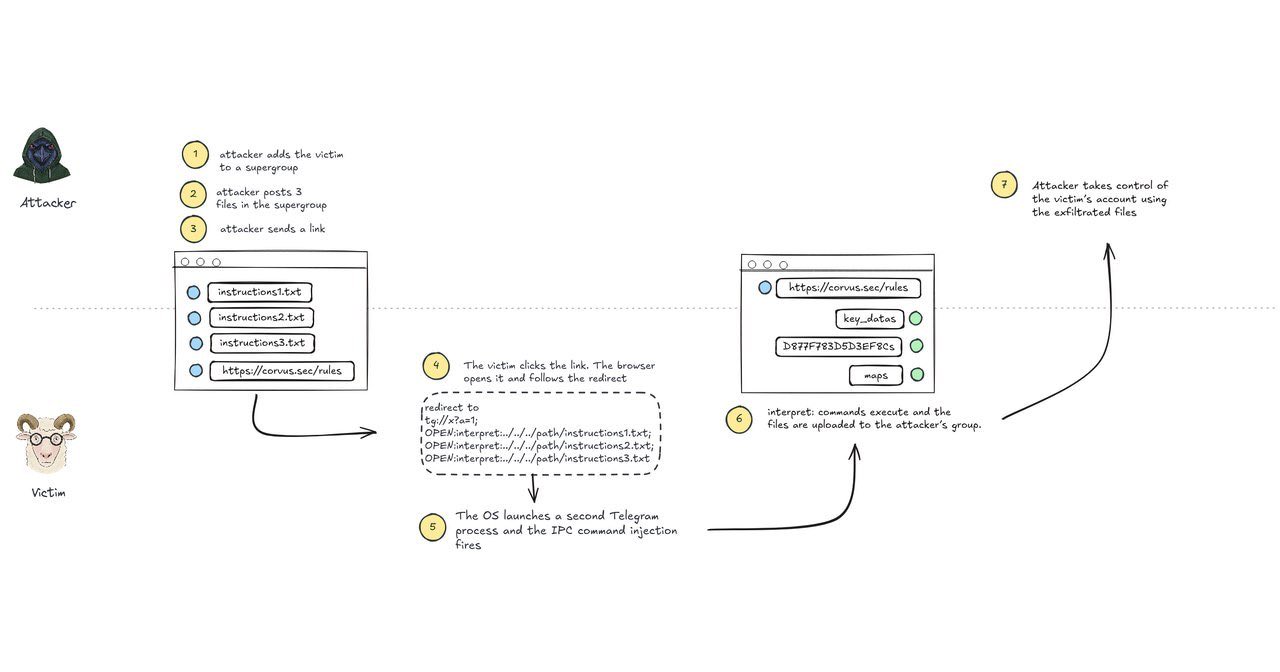
𝕏/@officer_secret ·
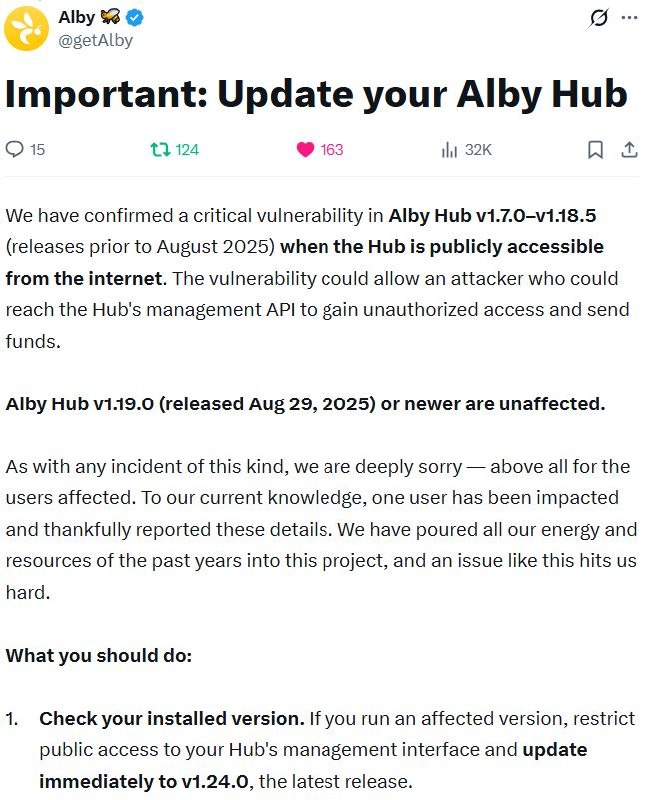
𝕏/@getAlby ·
near.ai ·
𝕏/@Cloudflare ·
𝕏/@initia ·
𝕏/@claudeai ·
𝕏/@officer_secret ·
𝕏/@getAlby ·