Frok discord appears to be compromised
𝕏/@kaizen_stark •
Revision history
3 recorded changes
Want your article here?
Promote with Leviathan News3 recorded changes
Want your article here?
Promote with Leviathan NewsOn 7 June 2024, the account of X user @kaizen_stark warned that the Frok project’s official Discord server appeared to be compromised, telling users not to interact with new links or messages and to treat the server as unsafe until the team confirmed control was restored. Subsequent community replies described typical compromise patterns seen in Web3 Discord attacks, including unexpected announcements and suspicious links that resembled phishing or wallet-draining attempts, though there was no formal post-mortem from the Frok team at the time of the alert. This incident fits a broader pattern of Discord compromises targeting crypto and NFT communities, where attackers obtain admin or bot credentials and push malicious links to users in a short time window. In such situations, security guidance from Discord and security providers generally recommends immediately treating the server as hostile, avoiding all links and “connect wallet” prompts, revoking any recent approvals, and waiting for an official recovery statement from verified project channels before re-engaging. The reported Frok Discord compromise therefore matters mainly as a reminder of this recurring attack vector and the ongoing need for hardened admin security and user skepticism around unexpected calls to sign transactions or mint from Discord. X/@kaizen_stark post on Frok Discord compromise General explanation of how Discord accounts get hacked and tokens stolen Discord support guidance on compromised accounts Third‑party best practices for responding to a hacked Discord account
AI-generated background, compiled from web sources — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Loading comments…
Restoring your session before loading comments…
𝕏/@PrityAfroz18740 ·
Reuters ·
𝕏/@AscendLaunch ·
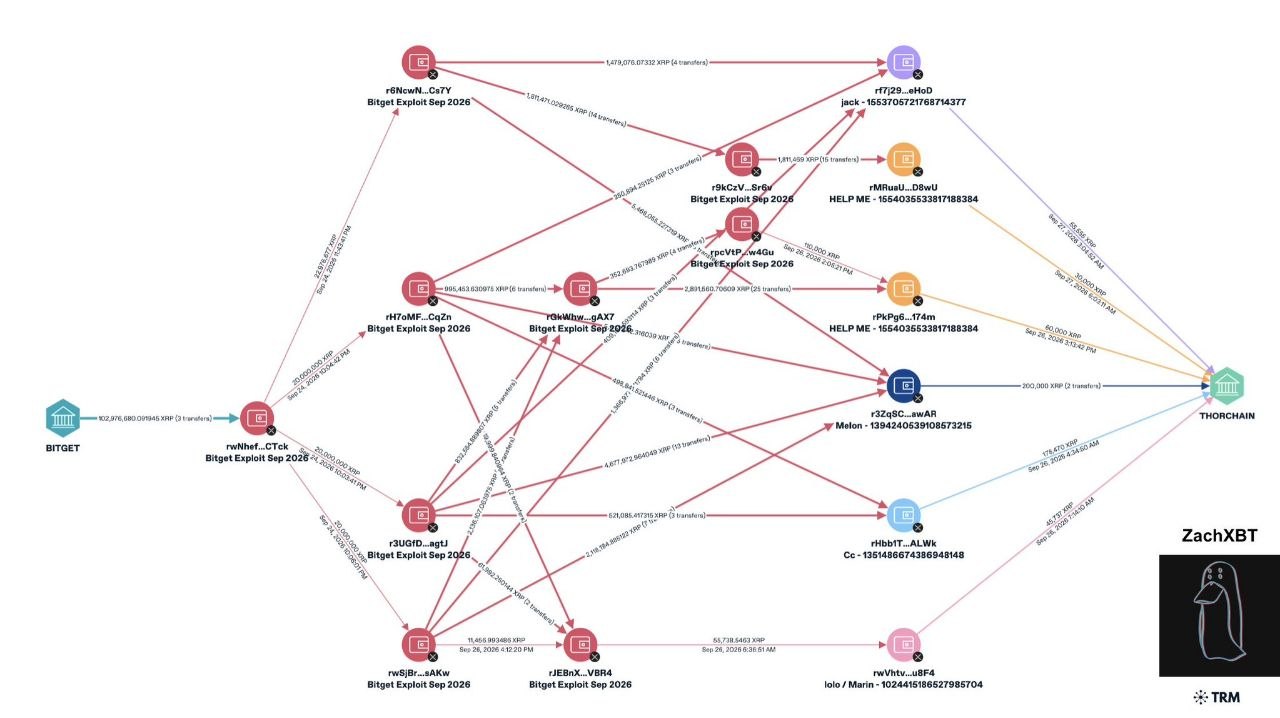
𝕏/@zachxbt ·
𝕏/@cancore_io ·
𝕏/@AdEx_Network ·
𝕏/@PrityAfroz18740 ·
Reuters ·
𝕏/@AscendLaunch ·
𝕏/@zachxbt ·
𝕏/@cancore_io ·
𝕏/@AdEx_Network ·