Radiant Capital hack post-mortem analysis
Medium •
Revision history
3 recorded changes
Want your article here?
Promote with Leviathan News3 recorded changes
Want your article here?
Promote with Leviathan NewsRadiant Capital, a cross-chain lending protocol, published a detailed post‑mortem on a major October 16, 2024 security incident in which attackers stole over $50 million in crypto assets and forced the protocol to pause operations. The investigation found that the core issue was not a smart contract bug but a targeted compromise of contributors’ devices and private keys, which allowed the attacker to control enough signers on Radiant’s 11‑member multisig to execute malicious upgrades and drain funds from lending pools on Arbitrum and BNB Chain. Developers were using hardware wallets and were geographically distributed, indicating a coordinated malware‑based campaign rather than physical coercion. The incident followed a separate ~$4.5 million flash‑loan‑related exploit earlier in the year, making this Radiant’s second major security failure in 2024. According to the post‑mortem and external technical analyses, the attacker first gained control of at least 3 of 11 multisig signers, which was the threshold required to authorize upgrades. With that control, they transferred ownership of Radiant’s pool provider contracts to a malicious implementation, upgraded the proxy logic, and then drained assets including USDC, USDT/BUSDT, BTCB, wBETH, wBNB, and ETH from user pools. Radiant coordinated with blockchain security firms, paused markets on impacted networks, and engaged U.S. law enforcement and the FBI to trace funds and investigate the malware and key compromise. The post‑mortem emphasizes operational security lessons for DeFi teams, including the risks of low multisig thresholds, the need for hardened key management and device security, continuous monitoring of admin actions, and defense‑in‑depth for multi‑chain treasury and governance controls.
AI-generated background, compiled from web sources — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Loading comments…
Restoring your session before loading comments…
𝕏/@binance ·
decrypt.co ·
NY Times ·
𝕏/@deitaone ·
𝕏/@binance ·
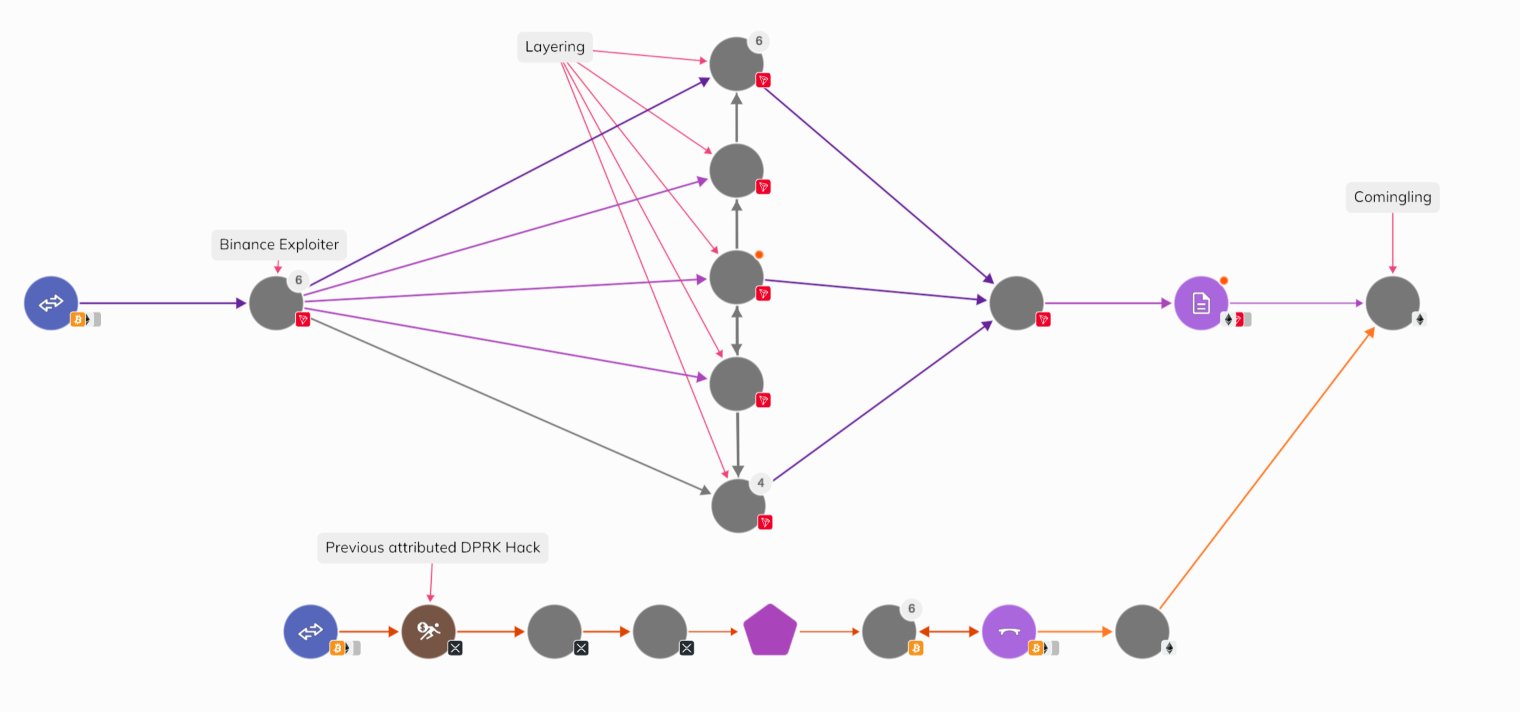
Chainalysis ·
𝕏/@binance ·
decrypt.co ·
NY Times ·
𝕏/@deitaone ·
𝕏/@binance ·
Chainalysis ·