UPDATE: Ledger details how an unauthorized implant in CryptoBilis-sold signers allegedly captured recovery phrases and transmitted them over LTE
𝕏/@Ledger •
Revision history
6 recorded changes
Want your article here?
Promote with Leviathan News6 recorded changes
Want your article here?
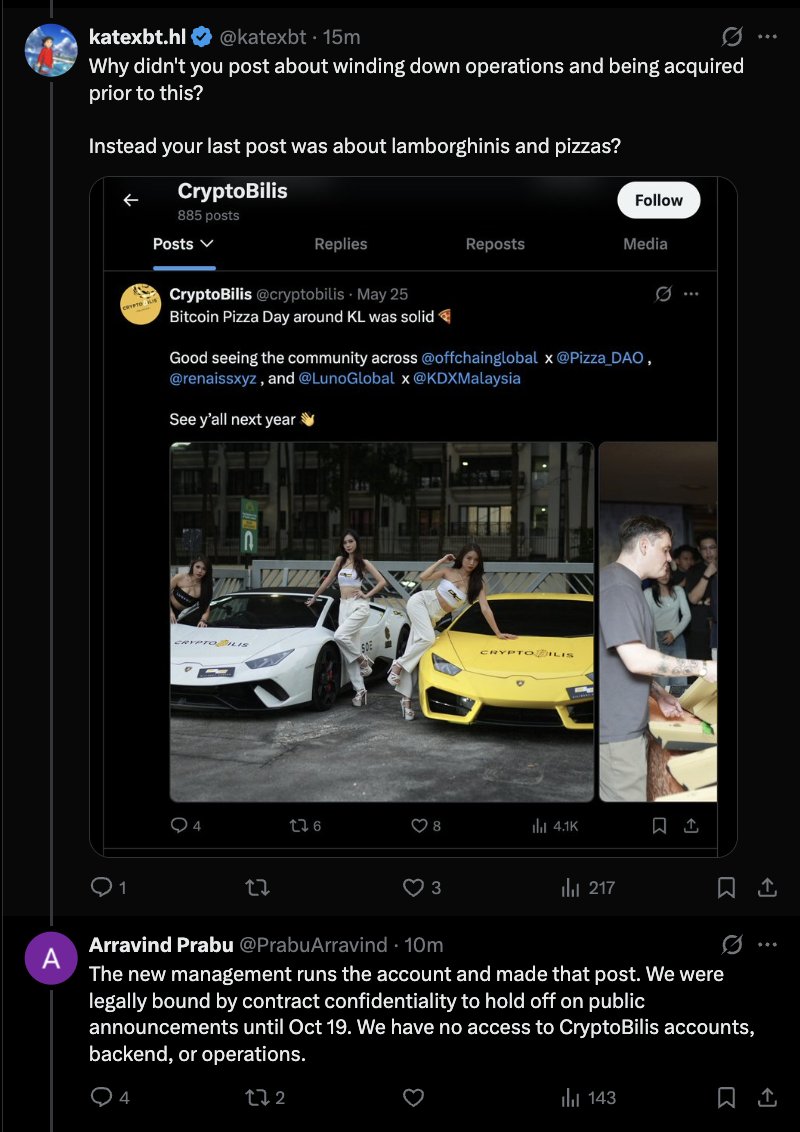
Promote with Leviathan NewsLedger Donjon's investigation found the implant sits inside the enclosure and reads screen data; during setup it decodes the displayed 24-word recovery phrase and transmits it over LTE via a provisioned eSIM. It is a separate component that does not modify the Secure Element or Ledger OS, and does not alter transactions or signatures. All confirmed losses tied to the October 9th disclosure involve signers sold through CryptoBilis, which has stopped selling Ledger signers. Ledger has not confirmed total affected users or value lost, saying circulating figures are unverified third-party numbers.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
Restoring your session before loading comments…
𝕏/@Ledger_Support ·
𝕏/@fatmanterra ·
𝕏/@Ledger_Support ·
𝕏/@ledger_business ·
𝕏/@Payward ·
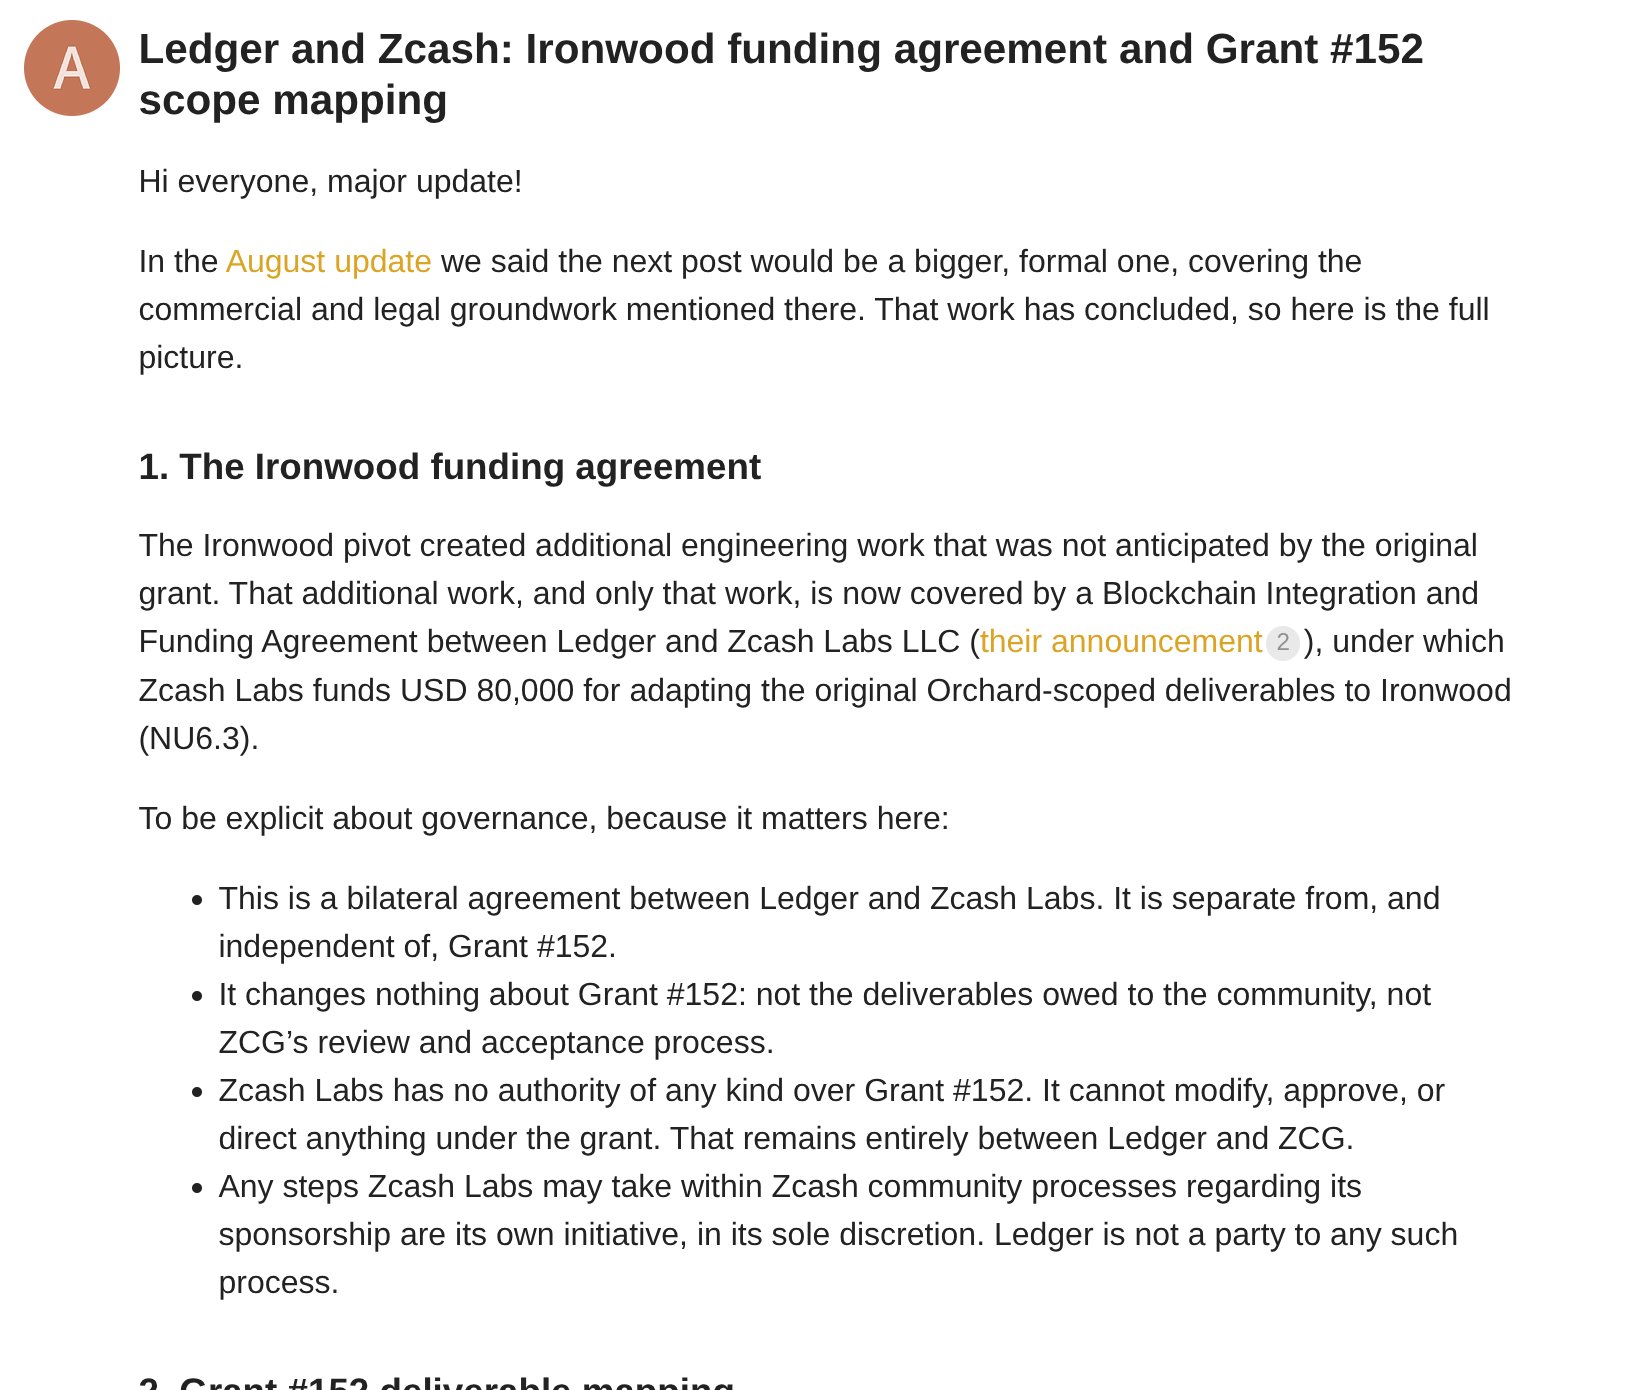
𝕏/@ZcashLabs ·
𝕏/@Ledger_Support ·
𝕏/@fatmanterra ·
𝕏/@Ledger_Support ·
𝕏/@ledger_business ·
𝕏/@Payward ·
𝕏/@ZcashLabs ·