Private keys compromised: HTTPS certificates for any website can be forged. Stay safe.
𝕏/@IntCyberDigest •
Revision history
2 recorded changes
Want your article here?
Promote with Leviathan News2 recorded changes
Want your article here?
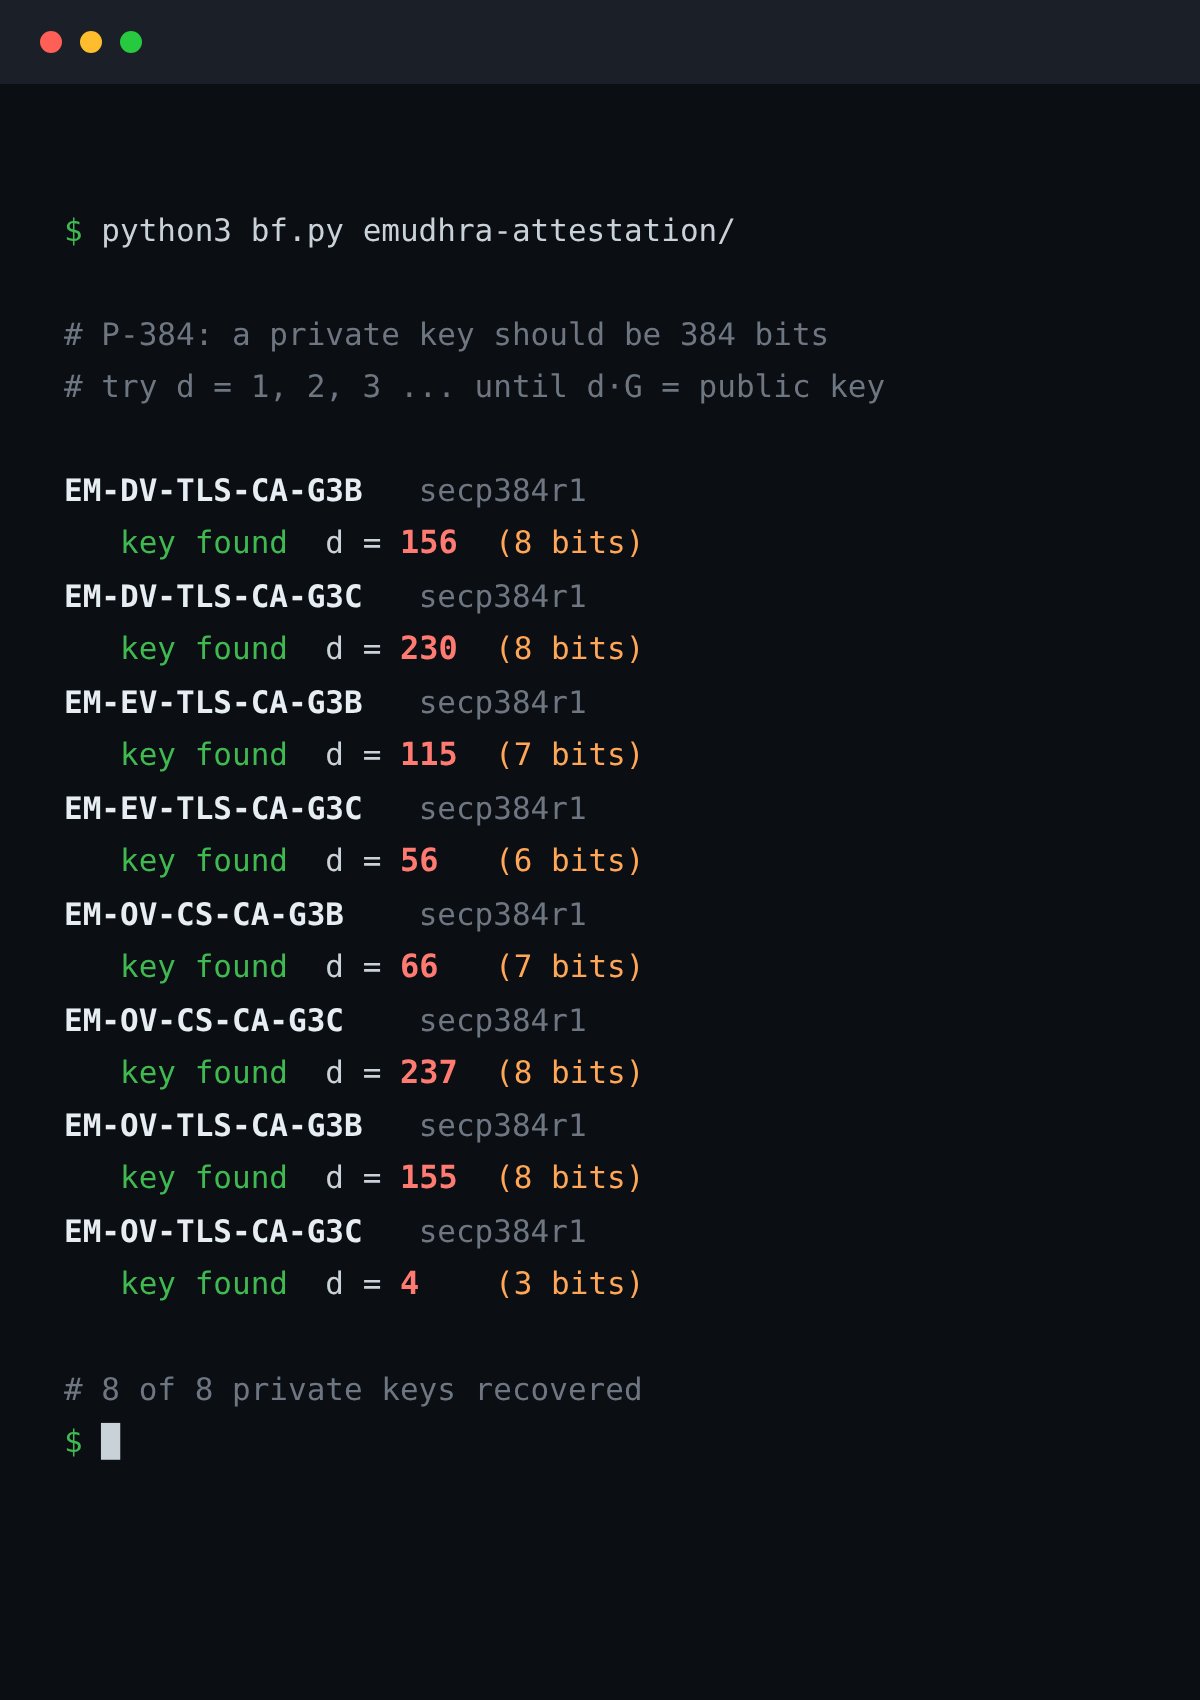
Promote with Leviathan NewsMozilla reports that private keys belonging to eight certificates issued by Indian certificate authority eMudhra were compromised. Firefox blocked the affected certificates within three hours of the disclosure. According to the post, one of the keys was only 4 digits long, while each should be a 116-digit number. The author warns that such weak keys can be guessed, allowing anyone to forge HTTPS certificates for any website.
AI summary of the linked source — not editorial content.
First post (Leviathan +3.9 h later) · @DailyDarkWeb · @moo9000 · @The_Cyber_News
Social-monitoring data, not investment advice Elfa post text from Xas of
Loading related coverage…
Loading comments…
𝕏/@jumperapp ·
crypto.news ·
𝕏/@officer_secret ·
𝕏/@DefimonAlerts ·
𝕏/@PeckShieldAlert ·
𝕏/@DefimonAlerts ·
𝕏/@jumperapp ·
crypto.news ·
𝕏/@officer_secret ·
𝕏/@DefimonAlerts ·
𝕏/@PeckShieldAlert ·
𝕏/@DefimonAlerts ·
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Danicjade
it just had to be from india 😂