Trezor raises wallet passphrase limit from 50 to 128 characters, citing Coldcard attacks
CoinTelegraph •
Revision history
4 recorded changes
Want your article here?
Promote with Leviathan News4 recorded changes
Want your article here?
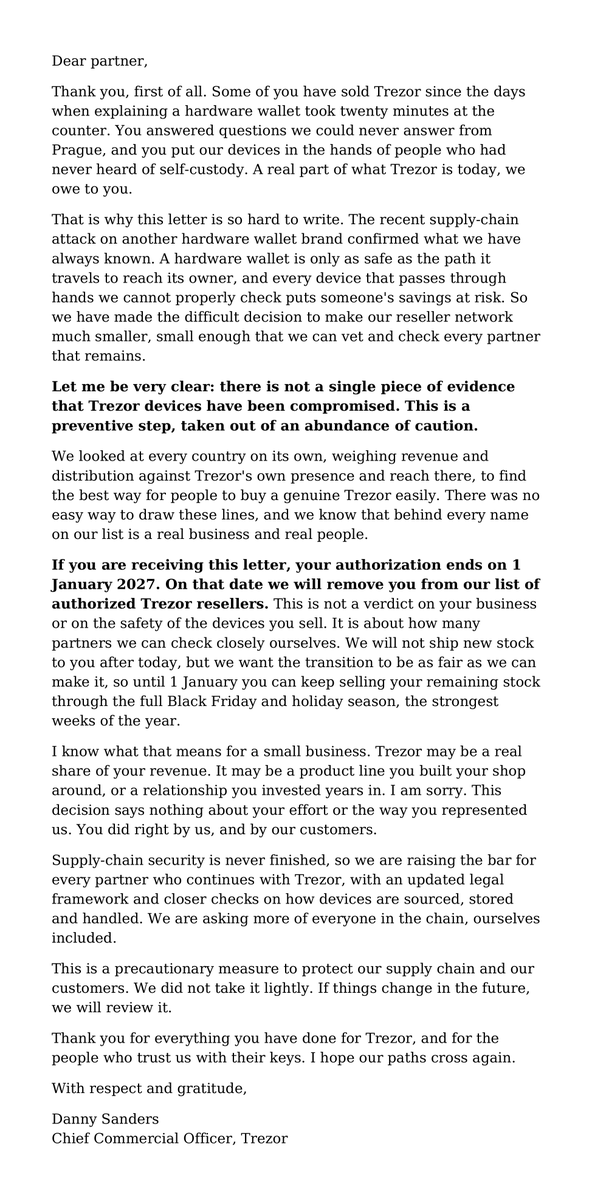
Promote with Leviathan NewsTrezor says the change requires updated device firmware; older firmware still caps passphrases at 50 characters. A passphrase works as an extra password alongside the recovery phrase, so an attacker with the phrase still needs it to access funds. Trezor cited July's Coldcard attacks, where a firmware flaw produced recovery phrases with insufficient randomness that attackers could reconstruct; strong passphrases protected some users. Separately, on Friday Trezor advised customers who bought wallets from former reseller CryptoBilis since March to move funds, after an Indonesian customer reported a suspected implant in a Trezor Safe 5 that could capture and transmit recovery phrases. Trezor said it had not examined that device and knew of no related losses.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Restoring your session before loading comments…
trezor.io ·
𝕏/@Trezor ·
𝕏/@Dantoshi ·
𝕏/@Trezor ·
𝕏/@Trezor ·
The Block ·
trezor.io ·
𝕏/@Trezor ·
𝕏/@Dantoshi ·
𝕏/@Trezor ·
𝕏/@Trezor ·
The Block ·