Coinbase NFT and OpenSea address security concerns in response to Thirdweb's disclosure of a critical vulnerability targeting NFT collections.
The Block •
Revision history
3 recorded changes
Want your article here?
Promote with Leviathan News3 recorded changes
Want your article here?
Promote with Leviathan NewsCoinbase NFT and OpenSea have moved to reassure users and creators after Web3 development platform Thirdweb disclosed a critical vulnerability affecting a widely used open‑source smart contract library for NFTs. Thirdweb said on December 4, 2023 that it had identified the issue on November 20 in a “commonly used” library integrated into some of its own pre-built contracts, including NFT drop and airdrop contracts using ERC20, ERC721, and ERC1155 standards. The flaw could potentially be exploited in impacted contracts created before November 22, 2023, although Thirdweb reported no evidence that its own contracts had been exploited. Because Thirdweb’s contracts underpin a number of NFT collections and drops, including some hosted via OpenSea and Coinbase NFT, both marketplaces issued statements outlining coordinated responses with Thirdweb. OpenSea said it was in contact with Thirdweb about the vulnerability affecting “some NFT collections” and is preparing to support creators who migrate to new, secure contracts. Coinbase NFT confirmed it was notified on December 1 that some collections deployed through Thirdweb on its platform were affected, but stressed that Coinbase’s core systems and customer funds remain safe. Thirdweb has published mitigation guidance and tools, advising affected contract owners to lock vulnerable contracts, take a snapshot of holders, and migrate to updated contracts, while marketplaces work to limit user impact and maintain trust in NFT infrastructure.
AI-generated background, compiled from web sources — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Loading comments…
Restoring your session before loading comments…
𝕏/@NMTD8 ·
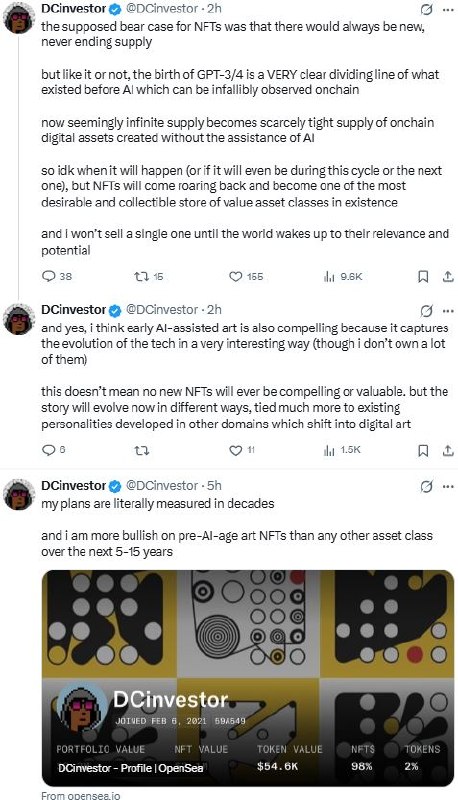
𝕏/@DCinvestor ·
𝕏/@0xquit ·
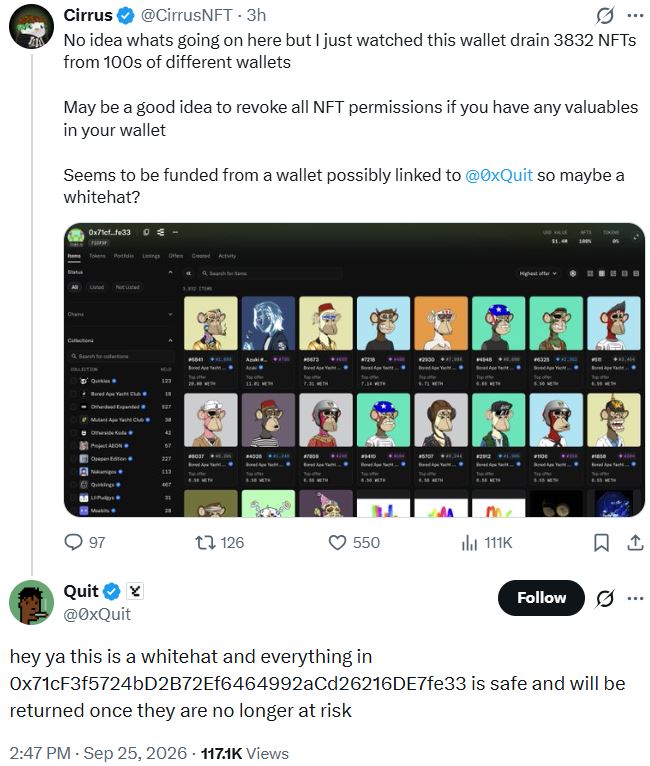
𝕏/@CirrusNFT ·
𝕏/@opensea ·

𝕏/@apechurch ·
𝕏/@NMTD8 ·
𝕏/@DCinvestor ·
𝕏/@0xquit ·
𝕏/@CirrusNFT ·
𝕏/@opensea ·
𝕏/@apechurch ·