Trezor says delivery partner Skladon breach exposed data for about 27,000 orders
𝕏/@Trezor •
Revision history
5 recorded changes
Want your article here?
Promote with Leviathan News5 recorded changes
Want your article here?
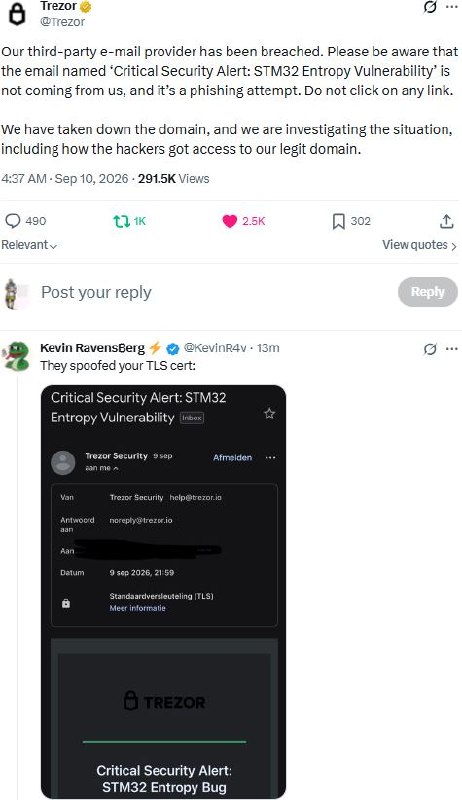
Promote with Leviathan NewsTrezor says data for about 27,000 orders placed between 9 August and 7 November was exported after an attacker gained unauthorized access at delivery partner Skladon, which notified Trezor on 15 November. Exposed fields include name, phone, address, email and order details; billing information was not included. Trezor says its own systems were not compromised and devices remain secure. Affected customers received an email; some who ordered 9–14 August cannot be reached because their details were anonymized. US customers are unaffected as Skladon does not ship there. Anonymous pickup is live in 18 European countries, retention falls from 90 to 45 days, and the investigation with Skladon continues.
AI summary of the linked source — not editorial content.
Loading related coverage…
Loading comments…
🚀 Love DeFi? Ready to dive in and start earning $SQUID while making an impact?
Loading comments…
Restoring your session before loading comments…
CoinTelegraph ·
trezor.io ·
𝕏/@Trezor ·
𝕏/@Dantoshi ·
𝕏/@Trezor ·
𝕏/@Trezor ·
CoinTelegraph ·
trezor.io ·
𝕏/@Trezor ·
𝕏/@Dantoshi ·
𝕏/@Trezor ·
𝕏/@Trezor ·